Discussion Locked
My Green Paste, Inc.
0 helpful
124 replies
Closed to new repliesThis discussion is closed. It stays readable, but it takes no new replies.
blog root

After Hours
... free electronic books.
http://www.microsoft.com/downloads/details.aspx?FamilyID=bcc70ccb-cf43-4dc8-807f-ea652a9538d3&displaylang=en is the download page for the full version of "Introducing Visual Basic 2005 for Developers"
http://www.microsoft.com/downloads/details.aspx?FamilyID=94BAAC98-6A0A-4FBB-9CC3-2534B671C299&displaylang=en is the download page for the full version of "Upgrading Microsoft Visual Basic 6.0 to Microsoft Visual Basic .NET".
I like the Image File Execution Options section of the registry. Many developers I've encountered aren't familiar with it, though. It's under-used, and that's a shame. (For some background on IFEO, check out http://blogs.msdn.com/junfeng/archive/2004/04/28/121871.aspx and http://blogs.msdn.com/greggm/archive/2005/02/21/377663.aspx.) So far, I've been able to use it for many things, including perhaps some things that it wasn't intended for. The most common value to set for a particular application is the "Debugger" REG_SZ value. This sets up another program to run as a debugger for the desired program. So, for example, if you set a "Debugger" value in HKLM\Software\Microsoft\Windows NT\CurrentVersion\Image File Execution Options\calc.exe to something like "devenv /debugexe", VS.NET would open up (provided DevEnv.exe is in the path), ready for you to begin a debugging session for Windows' Calculator program.
Now, depending on how you look at it, this can be good or it can be bad. Windows doesn't verify that the "debugger" is truly a debugger - it just spawns the application in the debugger value. This means that you can put "notepad.exe" in the debugger value under calc.exe, and every time you try to run "calculator", notepad will run instead. Mark Russinovich and Bryce Cogswell use this technique to implement the "Replace Task Manager" feature of their AWESOME Process Explorer utility (check out www.sysinternals.com for a LOAD of Really Useful utilities as well as other great info). Get Process Explorer, enable the option in the "Options" menu, and check HKLM\Software\Microsoft\Windows NT\CurrentVersion\Image File Execution Options\taskmgr.exe - the debugger value points to procexp.exe.
I've used IFEO to halt multi-part viruses and malware that continuously spawn multiple programs, where each component is responsible for, among other things, keeping other components alive. If the executables are predictably named, you can set a debugger entry for that exectable to run a "singleton" application (like regedit.exe, which allows only one instance of itself to be run under most conditions). Then you can kill the process and watch regedit open up. Do the same thing for the other bad program, and you can go about cleaning the system. Of course, this doesn't help in cases where the malware is fully contained in DLLs, but that's beyond the scope of this.
The other side of the above is that before too long, if it's not happening already, the malware authors will use IFEO to run their own junk. They could set a debugger value in HKLM\Software\Microsoft\Windows NT\CurrentVersion\Image File Execution Options\Explorer.exe, and that process would launch and then spawn Explorer. Or it could spawn BadProgram2.exe, then Explorer.exe, and then exit. This would be difficult to trace for a few reasons, one of which is how unknown the IFEO section of the registry is. I see that the most recent version of Sysinternals' AutoRuns (also by Mark Russinovich and Bryce Cogswell) - version 8.11 as I write this - adds detection of "image file hijacks", which I take to mean the very idea presented above. This is a good thing, but I hope it was added to be PROactive rather than REactive.
Another way I've used the "debugger" value for an executable in IFEO is to debug processes that run on other desktops. Inetinfo.exe (IIS), DLLHOST.EXE (COM+ apps), W3Wp.exe (IIS 6 World Wide Web Worker Process), and a slew of other programs can be "debugged" this way, even on production systems. Let's face it - how many times does the customer let you install a debugger on their system? :) . Even if you could install a debugger on a customer's system, if you set the debugger value in HKLM\Software\Microsoft\Windows NT\CurrentVersion\Image File Execution Options\W3Wp.exe to "devenv.exe /debugexe" and did something to kick off an instance of the World Wide Web Worker Process, VS.NET would start, but you probably wouldn't see it - the devenv.exe process would be running, but there would be no way to interact with it. Sometimes, you don't need to interactively debug the application to determine what the problem is. Enter Dependency Walker from www.dependencywalker.com . If you're able to get this relatively small (compared to debugger packages!) program on the system, just set up the debugger value of the desired process to something like:
"c:\path to\depends.exe" /c /pb /od:c:\temp\whatever.dwi
(run depends /? for a full description of available command line options)
This will cause Dependency Walker to be invoked when the desired process is to be started. "/c" tells Dependency Walker to run in "console mode", "/pb" tells it to profile the target application automatically, and "/od:" specifies that Dependency Walker should create a "DWI" (the native file format for Dependency Walker) file at c:\temp after the target application terminates. This is key - you need to wait for the application to terminate. So, for W3Wp.exe, you could unload the application from IIS Manager. At that point, the specified DWI file will be created, and it can be loaded into Dependency Walker (just run the program) via drag & drop, or File | Open. You can control some of the information captured by using the other "/p?" options, or you can run Dependency Walker, profile a dummy app (like calc.exe) and select all of the options you want for the next round - the help for Dependency Walker's "/p?" options states that "If this option is not specified, then the setting from the last time you ran Dependency Walker will be used". At any rate, you can do this if you need more info. I've used this technique to launch Dependency Walker to profile an app to determine what DLLs were missing or unreachable (path-wise) by the target process, or if the wrong version of the DLL was being picked up by the target process, or why a process was crashing.
Anyone else use these (or similar) tools/utilities? Anyone else use Image File Execution Options? Anyone know specifically how to interpret the ApplicationGoo REG_BINARY value of an entry in Image File Execution Options? It's related to "Application Compatibility", but...
... free electronic versions of the following books:
Introducing Visual Basic 2005 for Developers http://msdn.microsoft.com/vbrun/staythepath/additionalresources/IntroTo2005/default.aspx
Get all 8 chapters separately, or as one download.
Upgrading Microsoft Visual Basic 6.0 to Microsoft Visual Basic .NET http://msdn.microsoft.com/vbrun/staythepath/additionalresources/upgradingvb6/
Get all 21 chapters separately, or as one download.
I like the Image File Execution Options section of the registry.
Many developers I've encountered aren't familiar with it, though. It's
under-used, and that's a shame. (For some background on IFEO, check out
http://blogs.msdn.com/junfeng/archive/2004/04/28/121871.aspx and http://blogs.msdn.com/greggm/archive/2005/02/21/377663.aspx.)
So far, I've been able to use it for many things, including perhaps
some things that it wasn't intended for. The most common value to set
for a particular application is the "Debugger" REG_SZ value. This sets
up another program to run as a debugger for the desired program. So,
for example, if you set a "Debugger" value in
HKLM\Software\Microsoft\Windows NT\CurrentVersion\Image File Execution
Options\calc.exe to something like "devenv /debugexe", VS.NET would
open up (provided DevEnv.exe is in the path), ready for you to begin a
debugging session for Windows' Calculator program.
Now, depending on how you look at it, this can be good or it can be
bad. Windows doesn't verify that the "debugger" is truly a debugger -
it just spawns the application in the debugger value. This means that
you can put "notepad.exe" in the debugger value under calc.exe, and
every time you try to run "calculator", notepad will run instead. Mark
Russinovich and Bryce Cogswell use this technique to implement the
"Replace Task Manager" feature of their AWESOME Process Explorer
utility (check out www.sysinternals.com
for a LOAD of Really Useful utilities as well as other great info). Get
Process Explorer, enable the option in the "Options" menu, and check
HKLM\Software\Microsoft\Windows NT\CurrentVersion\Image File Execution
Options\taskmgr.exe - the debugger value points to procexp.exe.
I've used IFEO to halt multi-part viruses and malware that
continuously spawn multiple programs, where each component is
responsible for, among other things, keeping other components alive. If
the executables are predictably named, you can set a debugger entry for
that exectable to run a "singleton" application (like regedit.exe,
which allows only one instance of itself to be run under most
conditions). Then you can kill the process and watch regedit open up.
Do the same thing for the other bad program, and you can go about
cleaning the system. Of course, this doesn't help in cases where the
malware is fully contained in DLLs, but that's beyond the scope of this.
The other side of the above is that before too long, if it's not
happening already, the malware authors will use IFEO to run their own
junk. They could set a debugger value in
HKLM\Software\Microsoft\Windows NT\CurrentVersion\Image File Execution
Options\Explorer.exe, and that process would launch and then spawn
Explorer. Or it could spawn BadProgram2.exe, then Explorer.exe, and
then exit. This would be difficult to trace for a few reasons, one of
which is how unknown the IFEO section of the registry is. I see that
the most recent version of Sysinternals' AutoRuns (also by Mark
Russinovich and Bryce Cogswell) - version 8.11 as I write this - adds
detection of "image file hijacks", which I take to mean the very idea
presented above. This is a good thing, but I hope it was added to be
PROactive rather than REactive.
Another way I've used the "debugger" value for an executable in IFEO
is to debug processes that run on other desktops. Inetinfo.exe (IIS),
DLLHOST.EXE (COM+ apps), W3Wp.exe (IIS 6 World Wide Web Worker
Process), and a slew of other programs can be "debugged" this way, even
on production systems. Let's face it - how many times does the customer
let you install a debugger on their system? :) . Even if you could
install a debugger on a customer's system, if you set the debugger
value in HKLM\Software\Microsoft\Windows NT\CurrentVersion\Image File
Execution Options\W3Wp.exe to "devenv.exe /debugexe" and did something
to kick off an instance of the World Wide Web Worker Process, VS.NET
would start, but you probably wouldn't see it - the devenv.exe process
would be running, but there would be no way to interact with it.
Sometimes, you don't need to interactively debug the application to
determine what the problem is. Enter Dependency Walker from www.dependencywalker.com
. If you're able to get this relatively small (compared to debugger
packages!) program on the system, just set up the debugger value of the
desired process to something like:
"c:\path to\depends.exe" /c /pb /od:c:\temp\whatever.dwi
(run depends /? for a full description of available command line options)
This will cause Dependency Walker to be invoked when the desired
process is to be started. "/c" tells Dependency Walker to run in
"console mode", "/pb" tells it to profile the target application
automatically, and "/od:" specifies that Dependency Walker should
create a "DWI" (the native file format for Dependency Walker) file at
c:\temp after the target application terminates. This is key - you need
to wait for the application to terminate. So, for W3Wp.exe, you could
unload the application from IIS Manager. At that point, the specified
DWI file will be created, and it can be loaded into Dependency Walker
(just run the program) via drag & drop, or File | Open. You can
control some of the information captured by using the other "/p?"
options, or you can run Dependency Walker, profile a dummy app (like
calc.exe) and select all of the options you want for the next round -
the help for Dependency Walker's "/p?" options states that "If this
option is not specified, then the setting from the last time you ran
Dependency Walker will be used". At any rate, you can do this if you
need more info. I've used this technique to launch Dependency Walker to
profile an app to determine what DLLs were missing or unreachable
(path-wise) by the target process, or if the wrong version of the DLL
was being picked up by the target process, or why a process was
crashing.
Anyone else use these (or similar) tools/utilities? Anyone
else use Image File Execution Options? Anyone know specifically how to
interpret the ApplicationGoo REG_BINARY value of an entry in Image File
Execution Options? It's related to "Application Compatibility", but...
This one's been around a bit I'm sure, but it looks pretty cool:
http://www.nu2.nu/pebuilder/
Bart's Preinstalled Environment (BartPE) bootable live windows CD/DVD
"It will give you a complete Win32 environment with network support, a
graphical user interface (800x600) and FAT/NTFS/CDFS filesystem
support. Very handy for burn-in testing systems with no OS, rescuing
files to a network share, virus scan and so on."
Haven't had a chance to try it yet. That could be a good thing, or a bad thing... :)
On Windows XP and Server 2003, REGEDIT takes a command line parameter
that indicates a new instance should be opened up if an existing
instance is already running.
REGEDIT -m (or /m) does the trick...
I assume the 'm' is for "multiple"...
Recently, a developer was experiencing some odd behavior with MFC's
CFileFind class. It seems that it was returning files that didn't
match the wildcard pattern specified. The code was something like:
CFileFind finder;
BOOL bWorking = finder.FindFile( "0011????????.xxx" );
while( bWorking )
{
bWorking = finder.FindNextFile();
// ...
}
CFileFind uses the Win32 functions FindFirstFile and
FindNextFile. After working with various variations on filenames
that (to some extent) match the specified pattern, I was able to
determine that files with a name of 00117777.xxx were being
matched. OK... the doc on MSDN for FindFirstFile MSDN
states:
The search includes the long and short file names.
This gave me an idea. I created about 1000 files in the same
directory, with a name generated from a format string like 4454%08x,
and tested with my sample program. I got some hits in the search
for 0011????????.xxx! Turns out, Windows was creating 8.3
filenames for these files, and the generated 8.3 filenames were like
0011d4~1.xxx. The "false positives" were files which had short
file names that matched the desired pattern.
The developer is unable to rely solely on the results of the
FindNextFile call, and he has to do a sanity check to make sure that
every file that CFileCind indicates is a match, is truly what he's
looking for.
http://www.sysinternals.com/blog/2005/10/sony-rootkits-and-digital-rights.html
Looks like Mark Russinovich (Sysinternals) has found a DRM
protection scheme that hides itself using techniques commonly exhibited
by rootkits. There are a number of interesting issues raised around this matter...
Whoa... Ran across this a while ago, and again just this AM. But the first time I saw it was too late.
"When you restart a computer that is running Windows Server 2003 or Windows 2000
Server, the computer stops responding, or the "Applying computer settings"
screen appears for longer than you expect"
http://support.microsoft.com/?kbid=905716
Ran into a system where we could not install a service using the Win32
API CreateService (API would hang). We were also unable to delete
a service using DeleteService. Tried various techniques to
troubleshoot the problem, but the system wasn't even able to shutdown
gracefully. Thought there might be a virus so we had the admin of
the system run a scan. Nothing turned up. Wound up trying
INSTSRV from the Resource Kit. That too would hang. But I
used Dr. Watson to get a memory dump of the process and analyzed it in
WinDBG to verify that it, too, was hanging in CreateService. We
thought that perhaps there was something installed on the system that
was causing some sort of a conflict, so we tried to stop a number of
services on the system. Amazingly, none of the services would
stop - they would get into a state of "Stopping", and stay there.
Customer said they had other problems with the system, too, and were
considering replacing it. So we didn't do anything more with the
system. But one of the services I noted on the system that would
have problems from time to time was "APCPBEAgent"
(referenced in the above KB article) - it would sometimes remain in a
state of "Starting" for 5+ minutes. I suspect that the problems
with the system were a direct result of the issue outlined in the KB
article.
This problem occurs because of a problem with version
6.x of APC PowerChute Business Edition Software. APC has issued
the following official statement about this issue:
The APC 6.x software uses Sun Microsystems Java Cryptography
Extension(JCE) 1.2.1 Package. The digital certificate that was used to sign the
JCE 1.2.1 jar files expired on July 27, 2005. Because of this, the system causes
the above detailed symptoms.
Yuck.
http://forums.microsoft.com/MSDN/ShowPost.aspx?PostID=126606&SiteID=1
Microsoft has made the Visual Studio 2005 Express editions free for one year!
From the above link are links available to download:
Visual Web Developer 2005 Express
Visual Basic 2005 Express
Visual C# 2005 Express
Visual C++ 2005 Express
Visual J# 2005 Express
SQL Server Express
Download them before November 7, 2006, and they're free to use forever.
Linksys won't replace my BEFCMU10 cable modem even though Tech Support
led me on with talk of a 1-time replacement (out of warranty
replacement). The modem is nearly 3 years old, but why even
mention the 1-time replacement deal if it's only something they do for
30 days after the one-year warranty expires? Linksys seemed very
disorganized - like customer service didn't know what tech support was
doing, and vice versa. Not impressed. Also not impressed
when I asked the best way to dispose of the modem. Though she
later admitted she didn't know what was in the modem, she suggested
that I should just put it out with the garbage.
http://forums.cable-modem.net/index.php?action=vthread&forum=1&topic=253
Hmmm... Cisco. Doesn't Cisco own Linksys?
http://www.cisco.com/univercd/cc/td/doc/product/cable/cab_modm/ubr904/5360reg.htm#xtocid2519111
"Ultimate disposal of this product should be handled according to all national
laws and regulations"
From Motorola SB5100 manual:
http://broadband.motorola.com/consumers/products/SB5101/downloads/SB5101_UG_EN.pdf
"Recycling your Motorola Equipment
Please do not dispose of this product with your residential or
commercial waste. Some countries or regions, such as the European
Union,
have set up systems to collect and recycle electrical and electronic
waste items. Contact your local authorities for information about
practices established for your region. If collection systems are not
available, call Motorola Customer Service for assistance."
Apparently, Linksys makes cable modems that are environmentally friendly. Yeah, right.
I spent the better part of the day chasing down what was ultimately a check-box in Internet Explorer's Advanced options. Blech.
The problem was that IE was failing to load a user control, and not being very helpful in determining why the control wouldn't load.
The control would load properly using HTTP, but would fail under HTTPS. Sysinternals' Filemon and Regmon showed no anomalous behavior. Debugging with cordbg wasn't particularly useful - the information wasn't really pointing me anywhere. The IEHOST log file (http://support.microsoft.com/?kbid=313892) didn't provide much more than the fusion log, which contained:
*** Assembly Binder Log Entry (xx/yy/zzzz @ aa:bb:cc QM) ***
The operation failed.
Bind result: hr = 0x80070002. The system cannot find the file specified.
Assembly manager loaded from: C:\WINDOWS\Microsoft.NET\Framework\v1.1.4322\fusion.dll
Running under executable C:\Program Files\Internet Explorer\iexplore.exe
--- A detailed error log follows.
=== Pre-bind state information ===
LOG: Where-ref bind. Location = https://localhost/path/assemblyname.dll
LOG: Appbase = https://localhost
LOG: Initial PrivatePath = bin
LOG: Dynamic Base = NULL
LOG: Cache Base = NULL
LOG: AppName = NULL
Calling assembly : (Unknown).
===
LOG: Processing DEVPATH.
LOG: Policy not being applied to reference at this time (private, custom, partial, or location-based assembly bind).
LOG: Attempting download of new URL https://localhost/path/assemblyname.dll
LOG: All probing URLs attempted and failed.
And yet the IIS log was showing that the assembly was being requested and returned successfully to the client.
Eventually, I encountered the following KB article:
"How to run a user control assembly that is hosted on Internet Information Services (IIS) in Internet Explorer"
http://support.microsoft.com/?kbid=892466
which states:
"To successfully download a user control under these conditions, the client setting for the Do not save encrypted pages to disk setting must be cleared."
Simply clearing that check box allowed IE to download and instantiate the control.
Grumble.
The
other day, on a test server, ASP.NET was giving the following message:
Description: An error occurred during
the compilation of a resource required to service this request. Please review
the following specific error details and modify your source code appropriately.
Compiler
Error Message: CS0016: Could not write to output file
'c:\WINDOWS\Microsoft.NET\Framework\v1.1.4322\Temporary ASP.NET
Files\somepath\10d62725\cb6c7d34\k_kdx1bc.dll' -- 'Access is denied. '
Of course, it wasn't quite that simple. There was no problem
accessing that folder, as FILEMON from Sysinternals verified
when I set the filter to "Temporary ASP.NET Files". So I then
set the filter to CSC.EXE, and noted that it was failing with ACCESS DENIED on
C:\Windows\Temp\RES6.TMP running under NT AUTHORITY\NETWORK SERVICE. In
the C:\Windows folder, there was a TEMP folder, and a TEMP.DELETETHIS
folder. The ACL on the TEMP.DELETETHIS folder had an ACE for NETWORK
SERVICE, but the ACL on the TEMP folder did not. The creation date of the new
TEMP folder was roughly 1 week ago. So it appears that the installation
of ASP.NET added an ACE on the original TEMP folder that would allow ASP.NET /
NETWORK SERVICE to do what it needed to do. However, when someone decided
they wanted a new TEMP folder on the server, the new TEMP folder inherited the
permissions from WINDOWS and as such an ACE for NETWORK SERVICE was not placed
on the new folder. Renaming TEMP to TEMP.HOLD and renaming
TEMP.DELETETHIS back to TEMP solved the problem. Definitely an argument
for better change control on the servers, as well as potentially further
restricting access. But much of that is beyond my control...
At
any rate... the first hit in a google for CS0016
takes you to the MSKB which
almost nails it on the head, but in this case winds up kind of bending the nail so you have
to take the hammer and try to pound the nail upright again, and then... er...
nevermind.
Windows rootkits in 2005, part two
http://www.securityfocus.com/infocus/1851
I use Avant
Browser on multple systems. While it offers the ability to
import groups, it appears to only supoprt "CaptorGroup files" (*.cgp).
And there's no built-in way to export a group or groups. Sometimes, I
need to get groups from one system onto another. Since Avant Browser
stores groups in a "groups.dat" file located in
<%userprofile%\Application Data\Avant Browser\>, I can just grab
the group or groups I need out of groups.dat, save them to an
intermediate file, ensure that the "G" value is unique for the target
system, and append the group or groups to the groups.dat file on the
target system.
A sample section from groups.dat looks like the following. The aforementioned "G" value is "G10" below.
[G10]
Title=GroupName
NAME1=Url Name 1
LINK1=http://www.website1.com/index.htm
NAME2=Url Name 2
LINK2=http://www.website2.com/index.htm
Ran into this today. Not horribly noteworthy but it can bite you if you blindly click through the COM+ application export wizard.
http://support.microsoft.com/default.aspx?scid=kb;EN-US;873192
"You receive an "Error registering COM+ application" error message when you install an application proxy in COM+ 1.0"
"The Save application in COM+ 1.0 format - some properties may be lost option on the Application Export Information page must be enabled if you want to export your application proxy for COM+ 1.0. "
Windows XP and Windows Server 2003 run COM+ 1.5 and Windows 2000 runs COM+ 1.0.
Microsoft has a FAQ on Kernel Patch Protection for x64-based platforms running Windows Server 2003 Service Pack 1 and later.
http://www.microsoft.com/whdc/driver/kernel/64bitpatch_FAQ.mspx
http://clam.rutgers.edu/~lsobrado/graphicalpassword/
GraphicalPassword requires the .NET Framework 1.1. It's experimental, but an interesting concept. Your password is made up of specific icons. Many icons are presented and the idea is to find yours and click somewhere inside the perimeter created by extending imaginary lines out from your icons.
A corresponding article:
http://rutgersscholar.rutgers.edu/volume04/sobrbirg/sobrbirg.htm
Rumor has it that VMWare may soon start giving away their "lower-end" server virtualization product, GSX Server, for free. A pretty bold move, to be sure, but I think that it well serve them well. If people like GSX server they may be more inclined to upgrade to the higher-end product, ESX server, which doesn't require a host operating system.
Remote Desktop is a great feature, but sometimes you want to get to the console session on a remote system (rather than another, new session). The Terminal Services Console connection program (mstsc.exe) accepts some command line parameters, one of which is "console". This parameter allows you to connect to the console session on a server. If you run "mstsc /?", the "Usage" dialog displays, detailing more options.

This is golden:
Example
Defective Source
MmSecureVirtualMemory(NULL, 0, 0);
Corrected Source
// use something else
Thanks, Visual Studio .NET 2003!
Good thing it's only the life of a process at stake...
I've been working with a rather complex library of 3rd party COM components. One type-library is imported and there are a total of about 3,000 methods. As a result of what I presume to be the 3rd party not adhering to one of "The Rules of COM 101" ("published interfaces are immutable"), I'm kind of in a situation where I need to modify the code generated by the #import (the .tli file, at least).
I #imported the type-library with about 10 attributes to generate the .tlh and .tli files. Then I commented out the #import directive and just #included the .tlh, which in turn #includes the tli. In my case, I needed to modify the .tli so that instead of using the hard-wired DISPIDs that the compiler brought in with the #import, IDispatch::GetIDsOfNames is called to determine the DISPID at runtime. Of course, doing this more than once per program execution isn't efficient, so I wound up creating a local static DISPID variable to hold onto the value, and then a local static bool initialized to false to be the flag that indicates if the DISPID needs to be determined or not. To be thread safe, I entered a critical section prior to testing the bool, and leave the critical section immediately after determining that I've got the DISPID (either in this run, or in a previous one).
One attribute that came in handy in the #import is an undocumented one, "no_function_mapping". This attribute is mentioned in the MS KB article "Description of the no_function_mapping compiler directive and the implementation_key compiler directive in Visual C++ .NET or in Visual C++ 2005". Basically, the "no_function_mapping" attribute is used to disable the "implementation_key" compiler directive, which is used when a type-library has more than 1000 methods. In my case, I didn't need the "implementation_key" (in fact, it kind of cluttered the code) but apparently in other cases it actually causes compiler errors (documented in the KB article).
I don't usually advocate changing compiler-generated code but in this case I made an exception as I plan on thoroughly documenting what I did as well as WHY I did it, and how the idea can be carried forward should additional or newer methods in the 3rd party library be required.
Whoa.
This is over the top.
Words can't do it justice.
You just have to see it.
http://video.google.com/videoplay?docid=9151435244001559688
Insane.
Michael Howard has a good post about "Protecting against Pointer Subterfuge" and he introduces some functions that are new to Windows XP SP2 and Windows Server 2003 SP1:
EncodePointer and DecodePointer
EncodeSystemPointer and DecodeSystemPointer
A new version of Process Explorer from Sysinternals was released! Version 10.02 is a major upgrade and has a bunch of new features. Details and download (FREE!) are at:
http://www.sysinternals.com/Utilities/ProcessExplorer.html
Can't wait for Process Monitor!
ACK! What was Microsoft thinking? The .NET Framework 2.0 configuration tool (MSCORCFG.MSC Management Console) doesn't ship as part of the .NET Framework. Rather, it comes with the .NET Framework 2.0 SDK.
http://msdn2.microsoft.com/en-us/library/2bc0cxhc.aspx
In the .NET Framework versions 1.0 and 1.1, Mscorcfg.msc is installed with the .NET Framework redistributable package. Starting with the .NET Framework 2.0, Mscorcfg.msc is installed with the .NET Framework SDK.
This is a change from the .NET Framework 1.0 and 1.1, where the installation of the Framework put shortcuts in "Administrative Tools" for "Microsoft .NET Framework 1.1 Configuration" and "Microsoft .NET Framework 1.1 Wizards" for the .NET Framework 1.1, and similarly named tools for 1.0.
Sure, there are command-line tools that one can use to do much of the same things, but why remove the UI? The only thing I can think of is that if something's not there, someone can't play with it. But even if the Framework install lays down mscorcfg.msc, it wouldn't have to install a shortcut to it - that right there would probably keep 99% of the people away from the program. If someone needed it and knew it was there, they could browse to it and run it.
Seems odd. I hope to be able to do a bit more digging to find out why this tool isn't included as part of the base Framework install.
Looks like Windows XP SP2 and Windows Server 2003 (possibly only with SP1?) have added capabilities for logging information about DCOM activation failures and call failures. The document "Changes to Functionality in Microsoft Windows XP Service Pack 2" at http://www.microsoft.com/downloads/details.aspx?FamilyID=7bd948d7-b791-40b6-8364-685b84158c78&displaylang=en contains information about (among many other things!) the registry settings required to control the additional logging:
[HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Ole]
"ActivationFailureLoggingLevel"=dword:00000001
"CallFailureLoggingLevel"=dword:00000001
Setting the values to 0 turns the logging off. For the change(s) to take affect, the DCOM server needs to be restarted. This may require rebooting the system, depending on what the DCOM server is.
The settings cause the following types of messages to be logged to the System event log.
The machine wide limit settings do not grant Remote Access permission for COM Server applications to the user NT AUTHORITY\ANONYMOUS LOGON SID
(S-1-5-7). This security permission can be modified using the Component Services administrative tool.The machine wide limit settings do not grant Remote Activation permission for COM Server applications to the user NameSamCompatible SID ({sid}). This security permission can be modified using the Component Services administrative tool.
This allows one to determine what permissions need to be added to what accounts.
A knowledge base article that also documents these registry settings is:
Programs that use DCOM do not work correctly after you install Microsoft Windows Server 2003 Service Pack 1
Just opened an account up at Blogger.com; I intend to migrate my existing blog (which was kind of an experiment) to this blog, but I want to play around here a bit first. I anticipate this will be a bit more "natural" than the previous blogging service I was using. That's about it for now - I want to see what things look like and poke around a bit.
The other day, on a test server, ASP.NET was giving the following message:
Description: An error occurred during the compilation of a resource required to service this request. Please review the following specific error details and modify your source code appropriately.
Compiler Error Message: CS0016: Could not write to output file 'c:\WINDOWS\Microsoft.NET\Framework\v1.1.4322\Temporary ASP.NET Files\somepath\10d62725\cb6c7d34\k_kdx1bc.dll' -- 'Access is denied. '
Of course, it wasn't quite that simple. There was no problem accessing that folder, as FILEMON from Sysinternals verified when I set the filter to "Temporary ASP.NET Files". So I then set the filter to CSC.EXE, and noted that it was failing with ACCESS DENIED on C:\Windows\Temp\RES6.TMP running under NT AUTHORITY\NETWORK SERVICE. In the C:\Windows folder, there was a TEMP folder, and a TEMP.DELETETHIS folder. The ACL on the TEMP.DELETETHIS folder had an ACE for NETWORK SERVICE, but the ACL on the TEMP folder did not. The creation date of the new TEMP folder was roughly 1 week ago. So it appears that the installation of ASP.NET added an ACE on the original TEMP folder that would allow ASP.NET / NETWORK SERVICE to do what it needed to do. However, when someone decided they wanted a new TEMP folder on the server, the new TEMP folder inherited the permissions from WINDOWS and as such an ACE for NETWORK SERVICE was not placed on the new folder. Renaming TEMP to TEMP.HOLD and renaming TEMP.DELETETHIS back to TEMP solved the problem. Definitely an argument for better change control on the servers, as well as potentially further restricting access. But much of that is beyond my control...
At any rate... the first hit in a google for CS0016 takes you to the MSKB which almost nails it on the head, but in this case winds up kind of bending the nail so you have to take the hammer and try to pound the nail upright again, and then... er... nevermind.
OK... Last week Shawn Farkas (MS) blogged in the ".Net Security Blog" about "Which Package are the Security Tools In?" for the .NET Framework 2.0. In that post, he states they're in the SDK package, which was discussed previously. No direct reason is given, but in one comment an individual notes that GACUTIL is also not part of the redistributable package as was the case with the .NET Framework 1.1. To this, Shawn replies that "GAC administration is not an end-user scenario". One can consider that similar reasoning was applied to the moving of the .NET Framework 2.0 Configuration Tool from the redistributable package to the SDK. Still, the tools are at the least handy for troubleshooting and I can easily envision many cases where I will be wishing I had them available without having to install the SDK on another system.
I don't know that this needs much commentary. Name distorted to protect the guilty.
I've always liked this kind of thing. Over at Channel 9 on MSDN, they've got a "Knowledge Base Machine Translation Examples" wiki. The articles are RE-machine-translated back to English, so they're perhaps a bit worse than they would be if they'd only been machine-translated once.
Still, statements like the following are good fun:
A principle terrain must be truth to aquire the state of a physical printer
You show error 17803, if you execute a SORT- on a computer which has physical RAM multiple GB from SQL Server possesses,, or a CREATE INDEX operation on a computer,, which has physical RAM multiple GB from SQL Server possesses.
You engineers slogan are researching a resolution for this problem, which was denoted from user like you.
I love VMWare. Great product, innovative company. Recently had a minor problem after upgrading from Workstation 5.0 to 5.5, and wound up searching VMWare's knowledge base. Though I wasn't looking for this type of information at the time, I ran across an article that details a change one can make to a VM's configuration (.vmx) file that might improve performance. I haven't tried this yet, but plan on it the next time I have to move my VMs off of my laptop HD to an external HD (or *GULP* a network drive - yeah, yeah - I know).
Basically, VMWare uses a file in the VM's directory as a memory swap file. USB devices read and write data more slowly than internal HDs. So, VMWare uses a swap file on the USB device, and performance suffers. The suggested fix is to add the following setting to the VM's .vmx file:
mainMem.useNamedFile=FALSE
This tells VMWare to use the host system's HD to store the swap data.
The VMWare KB article is "Virtual Machine on USB or Other Slow Storage Device Runs Slowly".
I've been tasked with creating an installation program that handles installing some drivers in anticipation that a certain piece of hardware will be connected to the computer. The objective is to automate as much of the driver installation and subsequent driver selection as possible, with the ideal goal being that the user doesn't have to do anything other than run the program and then connect the device.
Should be pretty simple. But given that I'm not versed in the Windows Installer technology, and InstallShield is as foreign as Baklava to me... Let's just say that I'm learning a lot. The initial cut of drivers (from a 3rd party, also responsible for the device) wasn't signed so there wasn't much I could do on XP / Server 2003 to make the process totally automated. But I got things as streamlined as possible. Then, out of the blue, and kind of in a fit of irony, we "magically" got signed drivers. The changes to the installation procedures were moderate (new files, new file names, fewer drivers, etc). But the recommended installation steps (provided by the 3rd party) were more tedious. After much trial and error, I've got things to the point again that there is nothing that the user needs to do other than run the program and plug the device in. The only problem is that the results are inconsistent - sometimes the driver appears to be associated with the device successfully, sometimes Windows says that I HAVE to reboot to get the driver / device working... and sometimes Windows says that there _may_ be a problem with the device. So it could be goofy drivers, or it could be a faulty device, or it could be...
All this led me down a path where I needed to know far more about the driver installation process than I suspected I would have to. But I found a great document at Microsoft's web site - Troubleshooting Device Installation with the SetupAPI Log File. It's chock full of vitamins and information. I didn't have time to digest the full document, but I immediately noted the section "Appendix A: Setting the SetupAPI Logging Level". I skimmed and found that I could set [HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\Setup\LogLevel] to 0x2000FFFF. This will specify "that everything should be logged and that the log file should not be flushed to disk after each message is written" (to %windir%\setupapi.log). So I set the registry value and ran the installation program, and plugged the device in. Windows detected the device, found the driver, did it's magic... and reported that Windows needed to be rebooted (desipte the fact that I could begin using the device immediately). I opened setupapi.log and indeed all kinds of stuff was logged, including an entry toward the end that indicated the system would need to be rebooted because of an "unknown reason". The following excerpt is from the setupapi.log:
@ 15:40:40.775 #V282 Add Service: Modified existing service "SERVICENAME".
@ 15:40:40.785 #T214 Install Device: Writing driver descriptive registry settings.
@ 15:40:40.785 #T216 Install Device: Restarting device.
@ 15:40:40.955 #T217 Install Device: Restarting device completed.
@ 15:40:40.985 #W165 Device "USB\VID_XXXX&PID_XXXX\XXXXXXXXXXXXX" required reboot: Device not started (unknown reason).
@ 15:40:40.985 #T222 Install Device: Calling 'RUNONCE'/'GRPCONV' items.
@ 15:40:40.995 #I121 Device install of "USB\VID_XXXX&PID_XXXX\XXXXXXXXXXXXX" finished successfully.
@ 15:40:40.995 #T201 Install Device: End.
@ 15:40:40.995 #V156 Completed default installer.
@ 15:40:40.995 #V166 Device install function: DIF_NEWDEVICEWIZARD_FINISHINSTALL.
@ 15:40:41.005 #V155 Executing default installer.
@ 15:40:41.005 #V156 Completed default installer.
So either the driver's goofy or the device has issues. We don't really have control over either of them (3rd party), so there's not much that can be done in this particular case. But at least it seems I'm able to accomplish the ideal scenario if the device and the drivers behave properly.
Another interesting tidbit from the "Troubleshooting Device Installation with the SetupAPI Log File" document, again relating the the "LogLevel" registry setting:
Caution
Do not use 0xFFFFFFFF. This level turns on all logging, which results in an unreadable log file and some very slow installations.
Junfeng Zhang has a good description of GAC Assembly Trace References. I find it interesting that an assembly that has been placed in the GAC by Windows Installer cannot be removed unless the application that placed the assembly in the GAC is uninstalled. If one tries to remove an assembly from the GAC that was installed by Windows Installer with GACUTIL (gacutil -u assemblyname), GACUTIL reports:
Unable to uninstall: assembly is required by one or more applications
Pending references:
SCHEME: ID: DESCRIPTION :Number of items uninstalled = 0
Number of failures = 0
If one uses the Explorer Shell Extension for %windir%\Assembly, it
reports:
Assembly 'assemblyname' could not be uninstalled because it is required by other applications.
My primary system is a laptop. My schedule typically doesn't offer the ability to have long "computing" sessions. Rather, I get 10 minutes here, 15 minutes there, etc. As such, I find hibernation to be indispensable. Open the lid, hit the button, and in under a minute, I'm back to where I last left off. After upgrading from 512 MB RAM to 1280 MB, I started having problems hibernating - I would close the lid on the laptop and if I walked by it several minutes later the power light would be slowly fading on and off, indicating that the computer was in "standby" rather than hibernating. Resuming the system would yield a black exclamation point inside of a yellow triangle in the Systray, with a bubble stating "Insufficient resources exist to complete the API."
Of course, this was less than useful. What API? What type of system resources? One could surmise the API to be PowrProf's SetSuspendState, but what about the resources? Process Explorer didn't show any process to be using anything more than one would expect it to (no NP pool hogs, no apparent handle leaks, etc). After this happened, "hibernate" would not be available as a "shut down" option. Only after rebooting would the option to hibernate become available again. And hibernate would work for a few days after a reboot. But then the little yellow triangle would pop up, and I'd have to reboot to get the hibernation function working again.
I finally got frustrated enough by this to start looking around on the Internet for people with similar problems. I ran into two discussions (here and here) about the problem, and the scenarios described often had several similarities to my scenario. Among them:
After weeding deep enough through the discussions, I found a link to a Microsoft Knowledge Base article - "The computer occasionally does not hibernate and you receive an "Insufficient System Resources Exist to Complete the API" error message in Windows XP with Service Pack 2, in Windows XP Tablet PC Edition 2005, or in Windows XP Media Center Edition 2005".
The article exactly described my problem, and indicates the presence of a hotfix. The downside:
A supported hotfix is now available from Microsoft, but it is only intended to correct the problem that is described in this article. Only apply it to systems that are experiencing this specific problem. This hotfix may receive additional testing. Therefore, if you are not severely affected by this problem, we recommend that you wait for the next Windows XP service pack that contains this hotfix.
To resolve this problem immediately, contact Microsoft Product Support Services to obtain the hotfix.
Of course, I'm severely affected by this problem. The batteries drain faster when the computer doesn't hibernate. Many people have stuffed their computer into bags / cases, thinking that they were hibernating. Imagine their surprise to find the system ready to cook eggs when they take the computer out of the bag, because the system was on (in "standby"), enclosed in a padded, tight case.
So, it looks like I'll have to try to get the patch from MS PSS. We'll see what happens...
This is probably covered in all kinds of documentation - release notes, read-me's, etc. While VMWare does support USB devices, it appears that only USB 1.1 is supported in the guest despite the fact that the host may support USB 2.0. VMWare KB article "Performance of Isochronous USB Devices in Workstation 5 Windows Virtual Machines" alludes to this...
I don't use USB devices with VMWare that much, but it's good that VMWare supports USB even if it's only 1.1.
I noticed the following post by "LennyBacon":
"Please Wait - Building a WaitScreen control for ASP.NET "
I had to read the title three times before I realized it wasn't a "BlueScreen control for ASP.NET".
Hey - that's maybe not such a bad idea - a BSOD .NET System.Web.UI.UserControl class! Something in the vein of Sysinternals' "BlueScreen Screen Saver" perhaps...
A project for a rainy day, I suppose...
Perhaps this is what happens when geeks turn to Marketing?
Hitachi has a Flash Animation about hard drives that use perpendicular recording technology, which is expected to enable the manufacture of hard drives with 10 times the capacity currently available.
Was one of those bits John Travolta???
This dude is over the top. I laughed for hours. I was not surprised.
http://www.themorningnews.org/archives/spoofs_satire/be_not_afraid.php
And I love this IKEA RPG walkthrough:
http://www.themorningnews.org/archives/how_to/the_nonexpert_ikea.php
"IKEA is a fully immersive, 3D environmental adventure that allows you to role-play the character of someone who gives a **** about home furnishings."
See part 1 and part 2 of this topic...
Discovered some more info on the .NET Framework 2.0 configuration tool. I was using various tools to try to figure out what the console was doing. Just running MSCORCFG.MSC would yield the following dialog: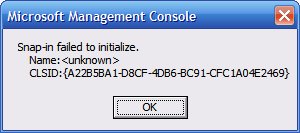
Obviously, something more needed to happen to get the MMC snap-in to work. I profiled MMC.EXE with Dependency Walker, and also monitored the process with FileMon and RegMon. I wasn't turning up much information. Then, in Dependency Walker, I noticed that MMC loaded MSCORMMC.DLL. MSCORMMC.DLL exported DllRegisterServer and DllUnregisterServer, so I figured that I needed to register the MSCORMMC.DLL with RegSvr32.
Running "regsvr32 mscormmc.dll" yielded the following series of dialogs: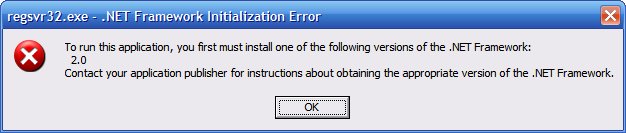

After thinking a bit, I decided to extract the files from the .NET Framework 2.0 SDK and open up netfxsdk.msi in InstallShield. I don't know what Micosoft uses to author its installation programs, but InstallShield sure had trouble with it - 100% CPU utilization when moving from component to component. It took a while, but I finally determined that doing "regsvr32 mscormmc.dll" actually put the wrong registry entries in place.
What follows is a .REG representing the "correct" registry entries that the installation program for the .NET Framework 2.0 SDK apparently takes care of. Note that all 3 paths to MSCORMMC.DLL would need to be changed to reflect the system that this REG file would be run on. Also note that the REG file removes any existing settings that might be there - in my tests it wasn't enough to simply merge the correct REG settings with the garbage left by doing "regsvr32 mscormmc.dll" - the old settings actually needed to be removed.
Windows Registry Editor Version 5.00
[-HKEY_CLASSES_ROOT\CLSID\{A22B5BA1-D8CF-4db6-BC91-CFC1A04E2469}]
[-HKEY_CLASSES_ROOT\CLSID\{D8FE614D-4851-4a72-998D-D1F2E750A050}]
[-HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\MMC\SnapIns\{A22B5BA1-D8CF-4db6-BC91-CFC1A04E2469}][HKEY_CLASSES_ROOT\CLSID\{A22B5BA1-D8CF-4db6-BC91-CFC1A04E2469}]
@="Microsoft.CLRAdmin.CData"[HKEY_CLASSES_ROOT\CLSID\{A22B5BA1-D8CF-4db6-BC91-CFC1A04E2469}\Implemented Categories]
[HKEY_CLASSES_ROOT\CLSID\{A22B5BA1-D8CF-4db6-BC91-CFC1A04E2469}\Implemented Categories\{62C8FE65-4EBB-45E7-B440-6E39B2CDBF29}]
@=""[HKEY_CLASSES_ROOT\CLSID\{A22B5BA1-D8CF-4db6-BC91-CFC1A04E2469}\InprocServer32]
@="C:\\Utils\\NetFW20Utils\\mscormmc.dll"
"ThreadingModel"="Both"
"Class"="Microsoft.CLRAdmin.CData"
"Assembly"="mscorcfg, Version=2.0.0.0, Culture=neutral, PublicKeyToken=b03f5f7f11d50a3a"
"RuntimeVersion"="v2.0.50727"[HKEY_CLASSES_ROOT\CLSID\{A22B5BA1-D8CF-4db6-BC91-CFC1A04E2469}\InprocServer32\2.0.0.0]
"Class"="Microsoft.CLRAdmin.CData"
"Assembly"="mscorcfg, Version=2.0.0.0, Culture=neutral, PublicKeyToken=b03f5f7f11d50a3a"
"RuntimeVersion"="v2.0.50727"[HKEY_CLASSES_ROOT\CLSID\{A22B5BA1-D8CF-4db6-BC91-CFC1A04E2469}\ProgId]
@="Microsoft.CLRAdmin.CData"[HKEY_CLASSES_ROOT\CLSID\{D8FE614D-4851-4a72-998D-D1F2E750A050}]
@="Microsoft.CLRAdmin.CAbout"[HKEY_CLASSES_ROOT\CLSID\{D8FE614D-4851-4a72-998D-D1F2E750A050}\Implemented Categories]
[HKEY_CLASSES_ROOT\CLSID\{D8FE614D-4851-4a72-998D-D1F2E750A050}\Implemented Categories\{62C8FE65-4EBB-45E7-B440-6E39B2CDBF29}]
@=""[HKEY_CLASSES_ROOT\CLSID\{D8FE614D-4851-4a72-998D-D1F2E750A050}\InprocServer32]
@="C:\\Utils\\NetFW20Utils\\mscormmc.dll"
"ThreadingModel"="Both"
"Class"="Microsoft.CLRAdmin.CAbout"
"Assembly"="mscorcfg, Version=2.0.0.0, Culture=neutral, PublicKeyToken=b03f5f7f11d50a3a"
"RuntimeVersion"="v2.0.50727"[HKEY_CLASSES_ROOT\CLSID\{D8FE614D-4851-4a72-998D-D1F2E750A050}\InprocServer32\2.0.0.0]
"Class"="Microsoft.CLRAdmin.CAbout"
"Assembly"="mscorcfg, Version=2.0.0.0, Culture=neutral, PublicKeyToken=b03f5f7f11d50a3a"
"RuntimeVersion"="v2.0.50727"[HKEY_CLASSES_ROOT\CLSID\{D8FE614D-4851-4a72-998D-D1F2E750A050}\ProgId]
@="Microsoft.CLRAdmin.CAbout"[HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\MMC\SnapIns\{A22B5BA1-D8CF-4db6-BC91-CFC1A04E2469}]
"About"="{D8FE614D-4851-4a72-998D-D1F2E750A050}"
"NameString"=".NET Framework 2.0 Configuration"
"NameStringIndirect"="@C:\\Utils\\NetFW20Utils\\mscormmc.dll,-30"[HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\MMC\SnapIns\{A22B5BA1-D8CF-4db6-BC91-CFC1A04E2469}\StandAlone]
@=""
(Let's hope the formatting of the REG file doesn't mess up the formatting of the whole blog...)
The files required are:
-- mscorcfg.dll
-- mscorcfg.msc
-- mscormmc11.cfg
-- mscormmc.dll
All files should be placed in the same directory (anywhere), but it appears that mscorcfg.dll also needs to be placed in the GAC. Again, note that the REG file above requires one to change the path to mscormmc.dll in 3 places to reflect the actual path to the DLL on the system on which the REG file is merged.
Found a page on the WHDC site at Microsoft.com that discusses using C++ in kernel mode drivers. Pretty interesting, for me at least. =8->
I've been getting involved recently in authoring installation programs. One of the things that comes up is how to determine what versions and service packs for the .NET Framework are installed. Usually, a "System Search" (in InstallShield) can be used to determine this. But what on the system should be searched?
There's this article from Macrovision / InstallShield that talks about the MsiNetAssemblySupport property available with Windows Installer 2.0 and later. The property uses the latest version of FUSION.DLL found on the system. The article then goes on to state:
Additional Information
For additional information, click the following link to view the article in the Microsoft Knowledge Base: http://support.microsoft.com/kb/318785
That KB article ("How to determine which versions of the .NET Framework are installed and whether service packs have been applied") provides a list of version stamps that correspond to a specific .NET Framework version and revision. The version stamps come from the MSCORLIB.DLLs that are installed by the various framework versions and revisions. So one is to search for all MSCORLIB.DLL files on the system and use the chart to determine what version(s) of the .NET Framework are installed.
Then, there's another MS KB article - "How to detect the installed version of the .NET Framework in a Visual Studio Setup and Deployment package" - that describes how to set up launch conditions in a Visual Studio Setup project to set properties based on the values of certain registry entries - specifically, entries residing in HKLM\SOFTWARE\Microsoft\.NETFramework\policy\vX.Y, where X is a major version and Y is a minor version number of the .NET Framework.
And finally, yet another MS KB article was published on 2006-02-28. This one is "How to use Visual C++ .NET to detect the .NET Framework versions and service packs that are installed on the computer". Again, one is instructed / directed to search in the registry for the answer. The keys referenced in this article are HKLM\Software\Microsoft\NET Framework Setup\NDP\vX.Y.Z, where X is a major version, Y is a minor version number, and Z is a "build" (or similar) number. For 1.1, and 2.0, that is. For 1.0, one is to check HKLM\Software\Microsoft\.NETFramework\Policy\v1.0 (like KB article 315291). To determine service pack levels, other registry values are checked.
Obviously, there are many different ways to do the same thing. But it would be nice if the MS KB was consistent. I think I prefer the method illustrated by "How to use Visual C++ .NET to detect the .NET Framework versions and service packs that are installed on the computer" because it seems the most straightforward - the registry value "Install" is set to 1 if the Framework version is installed, and the value "SP" is set to the level of the service pack of that version of the Framework that is installed. In this case, the .NET Framework 1.0 is a bit different, but it's pretty much a non-issue in my environment because we never officially released anything that ran on the .NET Framework 1.0.
The MS Patterns and Practices group has some free security training modules for developers. There's an intro at J.D. Meier's blog, and Channel 9 has the Patterns and Practices Security Training Modules Index. I haven't had the chance to check things out yet, but I sure would love to if I could find the time...
Ran across the following User-Mode Driver Framework (UMDF) resources:
UMDF drivers can run on Windows Vista. Support for UMDF on Windows XP is being considered for the Windows Vista release timeframe.
This is kinda cool.
LogParser from Microsoft Downloads is a pretty neat utility. Spend some time playing around with it, and it can be your best friend in a lot of cases.
The current version is 2.2.10, released on 2005-04-20.
There's even an easter egg in the program...
Run a CMD prompt, and change to the LogParser install directory (default is "C:\Program Files\Log Parser 2.2"). Then, type in (for example):
logparser "select * from c:\ntldr" -o:neuroview
The key, of course, is the parameter specifying the output format ("-0"), "neuroview" in this case.
I recently started seeing Event ID 4226 with source TCPIP (EVENT_TCPIP_TCP_CONNECT_LIMIT_REACHED) in my System event log. The message is "TCP/IP has reached the security limit imposed on the number of concurrent TCP connect attempts." It sounded familiar, so I figured I had seen it before and filed it away as a low priority item to deal with when I got the time.
I tore into it a bit more because it was starting to bother me a bit. I use Avant Browser's "Groups" feature to open 30 or so web pages multiple times a day. This is fine and dandy, but during the process where Avant is trying to load all of the pages, my system's network connectivity would go downhill. So I figured Windows was imposing some artificial limit on the number of outgoing TCPIP connections. Sure enough, "Changes to Functionality in Microsoft Windows XP Service Pack 2 - Part 2: Network Protection Technologies" indicates:
Limited number of simultaneous incomplete outbound TCP connection attempts
Detailed description
The TCP/IP stack now limits the number of simultaneous incomplete outbound TCP connection attempts. After the limit has been reached, subsequent connection attempts are put in a queue and will be resolved at a fixed rate. Under normal operation, when applications are connecting to available hosts at valid IP addresses, no connection rate-limiting will occur. When it does occur, a new event, with ID 4226, appears in the system?s event log.
Why is this change important? What threats does it help mitigate?
This change helps to limit the speed at which malicious programs, such as viruses and worms, spread to uninfected computers. Malicious programs often attempt to reach uninfected computers by opening simultaneous connections to random IP addresses. Most of these random addresses result in a failed connection, so a burst of such activity on a computer is a signal that it may have been infected by a malicious program.
What works differently?
This change may cause certain security tools, such as port scanners, to run more slowly.
How do I resolve these issues?
Stop the application that is responsible for the failing connection attempts.
The interesting thing is that there's nothing to change this behavior - you're limited to what appears to be 10 "concurrent TCP connect attempts".
Well, maybe it's more accurate to say that there's no Microsoft-sanctioned way to change this behavior. There _is_ a utility at http://www.lvllord.de/ that patches TCPIP.SYS and allows one to set the limit (default is 50, up from 10). Of course, this annoys Windows File Protection, and the patched TCPIP.SYS can be replaced by an update from Microsoft, but it appears the utility's author keeps the utility up-to-date so that in little or no time one can re-patch TCPIP.SYS if necessary.
It worked for me... :) Thanks, LvlLord!
VMWare posted a customer story to their website about curing "anemic CPU utilization". While I "get" it, I also thought it a bit atypical that a company would actually promote software that causes increased CPU usage.
int main( void ) {
while( 1 );
return 0;
}
OK... I don't know what motivated this, but Microsoft has made available hotfixes that can be used to change the time zone setting on Windows Server 2003 and Windows XP systems "in an organization". There is a hotfix for "(GMT-06:00) Central Time (US & Canada)" and one for "(GMT-05:00) Eastern Time (US & Canada)".
"Sometimes, you may want to change the Time Zone setting on many computers at the same time. This hotfix lets you change the Time Zone setting on a computer"...
Interestingly, the files in the hotfixes are named:
MakeMeCentral.dll
MakeMeEastern.dll
I wonder if we'll see a "MakeMeMountain"...
TechRepublic's "Path to existing blog's RSS feed" blog setting doesn't appear to be working - I've had to manually add the last 4 posts to my TR blog. Sigh. This might mean that when they fix it, there will be duplicate posts...
Microsoft has released the source code for "MechCommander 2" under its Shared Source license.
"This release contains all of the source code and source assets required to build MechCommander 2."
The intent is to use it with the "Microsoft XNA Build March 2006 Community Technology Preview (CTP)"
"Microsoft? XNA? Build is a tool which will help game studios manage the growing complexities of their game content builds. We invite you to install this pre-release into a non-production environment to learn more about how XNA Build will reduce development complexities."
Been a while since I've had a chance to get anything posted. But that doesn't mean that I haven't been collecting oodles of stuff that's just waiting for some attention... I've got a laundry list of things I'd like to blog about, and no time to really collect my thoughts and put together a coherent piece. In fact, some topics have been on the list so long they may not even be relevant, or I may not be able to recall what specifically I wanted to say. Senility++.
Altiris "is a worldwide company that has expanded its technology to provide affordable IT lifecycle management solutions for organizations of any size". (http://www.altiris.com/Company.aspx)
I recently had a chance to interact with a system that had Altiris software installed on it. I was digging through the system and I noticed a driver that didn't have a version resource associated with it. The name was "ALKERNEL.SYS". I did some more digging and found an interesting string in the binary: "ScottWroteThis!".
Scott, whoever you are, at least one person has acknowledged your efforts. Next time, toss a version resource in the driver along with some company info, and sign it while you're at it.
Oddly enough, the "Modified" timestamp on ALKERNEL.SYS seems to be updated with relative frequency... I think I'm going to have to see about doing some monitoring on this system, just to try and figure out what on earth is "updating" this file.
If you believe IE6's download progress indicator (and everyone does, right?), 27.6 MB is -3% of 3.12 GB. I was downloading Vista Beta 2 and, of course, was experiencing problems - the download servers were flooded. I didn't want to use the Akamai Download Manager, so I tried the "plain" method a few times and got this:
I finally resorted to the Akamai Download Manager. The results were much better. No, I didn't get a successful download for another 24 hours. But not having a negative progress indicator is an improvement...
Social Engineering, the USB Way describes an interesting social engineering tactic - leaving trojan-laced USB drives is easy to find places. The trojan would auto-run when plugged in to the computer, and "would collect passwords, logins and machine-specific information from the user's computer, and then email the findings back". The article describes this type of thing taking place at a credit union, but I would think the results would be similar almost anywhere.
The patch introduced to address the vulnerability described by Microsoft Security Bulletin MS06-032 (Vulnerability in TCP/IP Could Allow Remote Code Execution (917953)) drops a new TCPIP.SYS.
If you're using LvlLord's patch to change the half-open TCP limit from 10 connections to 50, you'll need to reapply.
From The Institute of Druidic Technology:
The
programming language used "Teutonic" runes (which, contrary to popular belief, were invented by the Druids for this purpose) for the elements of the language.
This is great stuff. I wonder if they ever did an ++...
Another morsel from the Institute of Druidic Technology - Rod Memory.
Unlike the bit, rods only have one state, as they are used to represent digits of the unary number system.
It is believed that rods which were broken, knobby or covered with moss or lichen aided in the eventual development of fuzzy logic.
The unary number system is covered at another Institute page, here.
From The Institute of Druidic Technology:
The
This is great stuff. I wonder if they ever did an ++...
The patch introduced to address the vulnerability described by Microsoft Security Bulletin MS06-032 (Vulnerability in TCP/IP Could Allow Remote Code Execution (917953)) drops a new TCPIP.SYS.
If you're using LvlLord's patch to change the half-open TCP limit from 10 connections to 50, you'll need to reapply.
From The Institute of Druidic Technology:
The
This is great stuff. I wonder if they ever did an ++...
Rather humorous comment by Bill Gates in 2003 about SPAM:
Like almost everyone who uses e-mail, I receive a ton of spam every day. Much of it offers to help me get out of debt or get rich quick.
Hehehe... The full article "Why I Hate Spam" is on Microsoft's site.
More quotes from Gates can be found in this ZDNet article.
Hehehe... This one makes me chuckle a bit. Now, realize it's a "Communuty Solution" contribution to the Microsoft Knowledge Base. That said, it _IS_ in the KB. And what precisely is IT? MS KB Article 555646, of course ("Modify the auto-restart time interval after a Windows update installation").
SYMPTOMS
...In the absence of user intervention, the computer is automatically restarted by Automatic updates and this can cause loss of unsaved user data.
CAUSE
This behavior in Windows XP with Service Pack 2 is by design and is not a bug.
So, the loss of unsaved user data is by design. Further, it is not a bug. It is not a bug in the design, and it is not a bug in the implementation of the design. It is entirely behaving the way it was intended. Don't ask questions. Don't pass go. Don't collect $C8.
Oh, by the way... It's not a bug, but there is a resolution. The resolution doesn't bring back the lost user data, though.
OK... As I go about my daily business, I track things that are noteworthy. Some things are things that I want to mention here, some warrant further consideration. Many of the things just seem to pile up because I don't have time to put something coherent together or because they require further exploration. Again, I am limited by available time.
In an attempt to "get stuff out there and shorten the list", I am going to try posting short blurbs where I can. I may do a few things at a time (probably in multiple postings). Because of the short-ish nature of these things, I expect that there will be an increase in the number of postings that have multiple "parts" to them.
We'll see how this works.
I am aware that this is a rather low-traffic blog. I never set out to make this a high-traffic, vigintillion-visitor place. No big deal. I do this for a few reasons...
I like it. I like exploring things and reporting my findings. Sometimes I get to dig deep into something. Other times something just strikes my fancy and I want to say "Hey - check this out."
I also use this blog as a form of documentation. I write about problems I have encountered, etc. I like troubleshooting problems. The solution to a problem isn't as helpful as it could be if it's withheld. I'm a details kind of person, so I tend to want to provide as much background and detail as possible about the situation I am describing. Odds are, I or someone else will run into the problem or situation again. When / if that happens, I can go back and find out what I did, what conclusion I came to, and how I got there.
They also say "the sound of your own voice must soothe you", so there may be some of that going on... ;)
I've been curious about who visits this blog. It's quite an interesting mix, actually. Well, interesting to me. Probably not all that different from similar blogs. Er... wait - there are no similar blogs. This is the only blog with this type of content. This is the only blog with this type of content. This is the only blog with this type of content. Yeah.
Anyway, I've had visitors from Microsoft, Sun Microsystems, various military branches and defense agencies, Fortis Bank, various software companies, Computer Sciences Corporation, various universities, airlines, and even a legal firm (which makes me perhaps a bit nervous)...
I'm interested in why people visit this blog, and what inspires them to leave comments on blogs in general. Anyone care to start? <g>
There's a settlement for a class-action lawsuit brought against Western Digital. The suit is based on the whole binary vs. decimal "controversy" - HD manufacturers measure capacity using the decimal number system while OS manufacturers use the binary number system.
Using the binary number system, 80 GB amounts to 85,899,345,920 bytes.
Using the decimal number system, 80 GB amounts to 80,000,000,000 bytes.
That's a difference of 5,899,345,920 bytes. Windows takes a drive with 80,000,000,000 bytes (as labeled by the drive maker) and displays it has having a capacity of about 74.4 GB.
Settlement details are at http://www.wdc.com/settlement/. WD "decided to settle to avoid a potentially expensive legal battle". The settlement includes back up /restore software and is available to those that have purchased a boxed WD HD between 2001-03-22 and 2006-02-15. Registration must be completed before 2006-07-16.
Very interesting explanation about why you shouldn't compress SQL Server log files and database files at http://blogs.msdn.com/khen1234/archive/2005/04/25/411852.aspx.
The obvious answer is performance, of course, but why performance suffers in this scenario is rather interesting. It's more than just the hit of compressing and decompressing the database data and log files. In short, when a compressed file is being read from or written to, IO operations are ALWAYS run synchronously.
This post originally appeared on an external website
Ran across some interesting videos.
Rocket exploding shortly after takeoff:
http://break.com/index/satblow.html
Liquid nitrogen + Swimming pool =??
http://www.collegehumor.com/movies/1695491/
In writing about the Western Digital "Hard Drive Settlement", I started wondering what brands of hard drives I had. I've got about 6 HDs in external enclosures, but they were in my office and I wasn't. I didn't want to open each case up to see what the drive was, and I didn't want to hook all of the drives up to the laptop.
Instead, I opened up a CMD window and at the prompt I typed "set DEVMGR_SHOW_NONPRESENT_DEVICES=1", hit enter, and then typed "devmgmt.msc" and hit enter again. This brought up Device Manager, as one might expect. I then selected "Show hidden devices" from the view menu.
This allowed me to expand the "Disk drives" category and see all of the "nonpresent" hard drives, which had at least some indication of the manufacturer in the name.
2 Seagates, 1 Maxtor, 1 Quantum, and 2 Western Digitals...
The child process (mmc.exe) inherits the environment space from the parent process (cmd.exe), and since the parent process had the environment variable DEVMGR_SHOW_NONPRESENT_DEVICES set, the child inherited that setting. Running devmgmt.msc started mmc.exe, the Microsoft Management Console executable which is associated with .MSC files. The .MSC instructed mmc.exe to load devmgr.dll, which contains the code to check the setting of the environment variable named DEVMGR_SHOW_NONPRESENT_DEVICES and react appropriately.
I got the following message from SQL Query Analyzer the other day when I was trying to debug a stored procedure on a development system:

Of course, I was unable to debug the stored procedure with the current confiuration. The SP would run, but one could not debug it. The "Event Viwer" (love the spelling) had no additional information, contrary to the message.
INF: Transact-SQL Debugger Limitations and Troubleshooting Tips for SQL Server 2000 and PRB: SQL Server Debugging with Visual Studio Service Pack 5 Requires a Non-System Account both mention a resolution to the problem ("Use the Domain User account (and not the Local System account) as the SQL Server service account and [make sure] that the Domain User account is a member of the Local Administrators group for remote debugging.") but the exact cause is not explained. Perhaps another day...
This post originally appeared on an external website
I was encountering a Windows Update error 0x8DDD0009 on a Windows 2000 SP4 system. I tried a number of things like stopping and restarting the Windows Update Auto Update service (wuauserv) rebooting, unregistering Windows Update-related components, etc. and nothing worked. Then I noticed the time on the system was off by about 22 minutes. I changed the time to be correct, and Windows Update magically started working again.
FWIW, 0x8DDD0009 can be interpreted to mean a lot of things...
Defined In: bthdef.h
Symbolic Name: BTH_ERROR_MAX_NUMBER_OF_CONNECTIONS
Defined In: bugcodes.h
Symbolic Name: IRQL_NOT_GREATER_OR_EQUAL
Defined In: cderr.h
Symbolic Name: CDERR_MEMALLOCFAILURE
Defined In: ceplog.mc
Symbolic Name: EVENT_MSCEP_FAILED_CA_CERT
Message: SCEP Add-on cannot retrieve CA's certificate (%2). %3 Please find support information at http://%1/certsrv/mscep/mscephlp.htm.
Defined In: certlog.mc
Symbolic Name: MSG_NO_POLICY
Message: The Certificate Services did not start: Unable to load an external policy module.
Defined In: cfgmgr32.h
Symbolic Name: CR_INVALID_NODELIST
Defined In: clusvmsg.h
Symbolic Name: LOG_MODULE_DM
Defined In: crypt32msg.mc
Symbolic Name: MSG_UNTRUSTED_ROOT_INFORMATIONAL
Message: Untrusted root certificate:: Subject: <%1> Sha1 thumbprint: <%2>
Defined In: dhcpssdk.h
Symbolic Name: DHCP_DROP_WRONG_SERVER
Defined In: dlcapi.h
Symbolic Name: LLC_STATUS_ADAPTER_NOT_INITIALIZED
Defined In: hidpddi.h
Symbolic Name: HIDP_GETCOLDESC_BYTE_ALLIGN
Defined In: iaapi.h
Symbolic Name: IAAPI_BADANY
Message: Bad ANY value
Defined In: iiscnfg.h
Symbolic Name: MD_ERROR_SUB403_TOO_MANY_USERS
Defined In: kerberr.h
Symbolic Name: KDC_ERR_NULL_KEY
Message: The client or server has a null key
Defined In: lpmapi.h
Symbolic Name: RSVP_Err_AMBIG_FILTER
Message: Ambiguous Filter spec in Resv
Defined In: lpmapi.h
Symbolic Name: POLICY_ERRV_GLOBAL_DEF_FLOW_DURATION
Defined In: mapidefs.h
Symbolic Name: MAPI_DIAG_PROHIBITED_TO_CONVERT
Defined In: mmsystem.h
Symbolic Name: MMSYSERR_BADERRNUM
Defined In: msaudite.h
Symbolic Name: SE_CATEGID_ACCOUNT_LOGON
Message: Account Logon
Defined In: msiquery.h
Symbolic Name: MSIDBERROR_BADGUID
Message: invalid GUID
Defined In: nb30.h
Symbolic Name: NRC_NORES
Message: no resource available
Defined In: nddeapi.h
Symbolic Name: NDDE_INVALID_ITEMNAME
Defined In: netmon.h
Symbolic Name: NMERR_DRIVER_NOT_FOUND
Defined In: ntdddisk.h
Symbolic Name: SMART_NOT_SUPPORTED
Message: Invalid cmd flag set
Defined In: odbcinst.h
Symbolic Name: ODBC_ERROR_INVALID_DSN
Defined In: ole.h
Symbolic Name: OLE_ERROR_METAFILE
Message: Invalid metafile
Defined In: pollog.mc
Symbolic Name: MSG_NO_REQUESTER_TOKEN
Message: The Enrollee was not able to successfully authenticate to the Certificate Service. Please check your security settings.
Defined In: routprot.h
Symbolic Name: MFE_NO_ROUTE
Message: router has no route that matches
Defined In: scesvc.h
Symbolic Name: SCESTATUS_ACCESS_DENIED
Defined In: snmp.h
Symbolic Name: SNMP_ERRORSTATUS_WRONGENCODING
Defined In: ssc.h
Symbolic Name: GE_SSC_ERR_INVALID_GE_STAGE
Message: GE internal error
Defined In: twain.h
Symbolic Name: TWCC_BADPROTOCOL
Message: Unrecognized MSG DG DAT combination
Defined In: w32timemsg.mc
Symbolic Name: MSG_TIMEPROV_FAILED_TIMEJUMP
Message: The time provider '%1' returned an error when notified of a time jump. The error will be ignored. The error was: %2
Defined In: wincrypt.h
Symbolic Name: CMC_FAIL_POP_FAILED
Defined In: winerror.h
Symbolic Name: ERROR_INVALID_BLOCK
Message: The storage control block address is invalid.
Defined In: winldap.h
Symbolic Name: LDAP_REFERRAL_V2
Defined In: winldap.h
Symbolic Name: LDAP_PARTIAL_RESULTS
Defined In: winsnmp.h
Symbolic Name: SNMP_ERROR_WRONGENCODING
This post originally appeared on an external website
Michael Howard writes about "a new defense against buffer overrun exploits called address space layout randomization" (ASLR) that is included in Windows Vista Beta 2. He also indicates that "it?s on by default too". Does this mean that it is possible to disable it? And if so will the ability to disable it make its way to the final release of Vista?
It seems that ASLR, combined with other strategies, will result in some significant improvements to the security of the Windows Vista platform. And personally, I don't see how it is relevant that various *nixz may have had this feature for a while. It just lends credibility to the decision to add the feature to Vista, I suppose.
?
It is an error to use a section registered as allowDefinition='MachineToApplication' beyond application level. This error can be caused by a virtual directory not being configured as an application in IIS. web.config 28
I tried a few things out, and examined the referenced web.config line, but nothing seemed out of the ordinary.
It took me a few minutes to figure out that I was looking at the wrong web.config. I had made a backup copy of the project (no SCCS yet - don't ask) in a subfolder. The web.config referenced in the error message was the backup copy, not the one belonging to the application I was working on. Removing the subfolder / project backup got rid of the message.
?
This post originally appeared on an external website
Microsoft Knowledge Base Article 923101 (Error message when you try to install security update 917283 on a computer that is running Windows Server 2003 x64 Edition: "Error 1324. The folder 'Program Files' contains an invalid character") details a heinous resolution to a problem installing the ASP.NET 2.0 patch covered in Microsoft Security Bulletin MS06-033 - Vulnerability in ASP.NET Could Allow Information Disclosure (917283).
Basically, one needs to "temporarily unmount any drive volumes that you do not require", and the article includes the steps one should go through. The step-by-step instructions only mention "CD-ROM and DVD drive volumes" - I wish the article was clearer on precisely which volumes should be unmounted. Anyway, the next step is installing the the 917283 update, followed by a possible reboot. The last step is to "remount the drive volumes" (assigning the CD-ROM and DVD drive volumes their original drive letters).
I would love to know what the real problem is, and how this fixes it.
Error 1324 (sometimes referenced as -1324) seems to correspond to "The path" or "The folder" or "The folder path" " contains an invalid character", which is the message described in article 923101. According to Windows Installer Error Messages, the message associated with 1324 is "The folder path '[2]' contains an invalid character".
Good thing 923101 only applies to x64 editions of Windows Server 2003.
?
This post originally appeared on an external website
Was having a very annoying problem with SQL Server 2000 on a development box the other day. I would stop MSSQLSERVER but when I tried to restart it, I couldn't:
C:\>net stop mssqlserver
The MSSQLSERVER service is stopping.
The MSSQLSERVER service was stopped successfully.
C:\>net start mssqlserver
The MSSQLSERVER service is starting.
The MSSQLSERVER service could not be started.
The service did not report an error.
That wasn't helpful so I turned to the Event Viewer where I found the following error events:
Event Type: Error
Event Source: MSSQLServer
Event Category: (8)
Event ID: 19011
Date: 7/25/2006
Time: 10:17:01 AM
User: N/A
Computer: COMPNAME
Description:
SuperSocket info: ConnectionListen(Shared-Memory (LPC)) : Error 5.
For more information, see Help and Support Center at http://go.microsoft.com/fwlink/events.asp.
Event Type: Error
Event Source: MSSQLSERVER
Event Category: (2)
Event ID: 17052
Date: 7/25/2006
Time: 10:17:01 AM
User: N/A
Computer: COMPNAME
Description:
Error: 17826, Severity: 18, State: 1
Could not set up Net-Library 'SSNETLIB'.
For more information, see Help and Support Center at http://go.microsoft.com/fwlink/events.asp.
Data:
[info containing computer name]
Event Type: Error
Event Source: MSSQLSERVER
Event Category: (2)
Event ID: 17055
Date: 7/25/2006
Time: 10:17:01 AM
User: N/A
Computer: COMPNAME
Description:
17120 :
SQL Server could not spawn FRunCM thread.
For more information, see Help and Support Center at http://go.microsoft.com/fwlink/events.asp.
Data:
[info containing computer name]
Probably, the first error was causing the next two. But what was really going on?
Sounded like something was hanging on to some handle or resource that SQL Server wanted. In search of more info, I checked out
C:\Program Files\Microsoft SQL Server\MSSQL\LOG\ERRORLOG which contained the following:
2006-07-25 10:17:01.38 server Microsoft SQL Server 2000 - 8.00.760 (Intel X86)
Dec 17 2002 14:22:05
Copyright (c) 1988-2003 Microsoft Corporation
Desktop Engine on Windows NT 5.1 (Build 2600: Service Pack 2)
2006-07-25 10:17:01.38 server Copyright (C) 1988-2002 Microsoft Corporation.
2006-07-25 10:17:01.38 server All rights reserved.
2006-07-25 10:17:01.38 server Server Process ID is 3640.
2006-07-25 10:17:01.38 server Logging SQL Server messages in file 'C:\Program Files\Microsoft SQL Server\MSSQL\LOG\ERRORLOG'.
2006-07-25 10:17:01.40 server SQL Server is starting at priority class 'normal'(1 CPU detected).
2006-07-25 10:17:01.40 server Performance monitor shared memory setup failed: -1
2006-07-25 10:17:01.66 server SQL Server configured for thread mode processing.
2006-07-25 10:17:01.66 server Using dynamic lock allocation. [500] Lock Blocks, [1000] Lock Owner Blocks.
2006-07-25 10:17:01.68 spid3 Starting up database 'master'.
2006-07-25 10:17:01.83 server Using 'SSNETLIB.DLL' version '8.0.766'.
2006-07-25 10:17:01.83 spid5 Starting up database 'model'.
2006-07-25 10:17:01.88 server SQL server listening on .
2006-07-25 10:17:01.88 server Error: 17826, Severity: 18, State: 1
2006-07-25 10:17:01.88 server Could not set up Net-Library 'SSNETLIB'..
2006-07-25 10:17:01.88 server Unable to load any netlibs.
2006-07-25 10:17:01.88 server SQL Server could not spawn FRunCM thread.
I'm guessing the "Performance monitor shared memory setup failed: -1" corresponded to the first message in the Event Log ("SuperSocket info: ConnectionListen(Shared-Memory (LPC)) : Error 5."), and the other two Event Log messages appear in the ERRORLOG.
This made it look like SQL Server couldn't acquire a resource (Access denied, according to the first Event Viewer message) related to shared memory used for performance monitoring. On a whim, I closed SQL Server Enterprise Manager and tried to start SQL Server again. This time, it worked.
The log details provide information that indicates that the system is running SQL Server 2000 SP3. The SQL Server 2000 SP4 Fix List doesn't include any descriptions that seem to indicate the problem is fixed in SP4, and I won't have the opportunity to apply SP4 any time soon to see so I suppose I'll just have to deal with it by closing Enterprise Manager before restarting SQL Server.
?
This post originally appeared on an external website
When signing an assembly, I prefer to use key containers rather than key files. Just specify a key name in AssemblyKeyName and the assembly is signed with that key provided that it has been installed on the machine. Installing the key into a key container is easy. Take the keyfile (keyfile.snk) obtained by running sn -k keyfile.snk from a Visual Studio / SDK Command Prompt and run it with sn -i keyfile.snk keycontainer. Set AssemblyKeyName in AssemblyInfo.cs to "keycontainer" ([assembly: AssemblyKeyName("keycontainer")]) and the assembly will be signed with the key in keycontainer.
At least, that's how it worked in Visual Studio .NET 2002 and Visual Studio .NET 2003. In Visual Studio 2005, if one uses the AssemblyKeyName attribute in AssemblyInfo.cs, one gets the following warning:
Properties\AssemblyInfo.cs(16,12): warning CS1699: Use command line option '/keycontainer' or appropriate project settings instead of 'AssemblyKeyName'
This is fine, except a reason we'll get into later. If one looks up C# compiler warning CS1699 in the VC# Reference, one will note that "Prior to Microsoft Visual C# 2005, you specified the key file using CLR attributes in source code. These attributes are now deprecated". The warning description goes on to list security, usability, and decreased compiler efficiency as reasons for the deprecation.
Now, the reference page for CS1699 also states "Beginning in Microsoft Visual C# 2005, you should use the Signing Page of the Project Designer or the Assembly Linker to specify the key". The problem here is that the "Signing Page" has no place to specify a key container!
CS1699's documentation points one to a page titled "/keycontainer (Specify Strong Name Key Container) (C# Compiler Options)". On that page one finds the following tasty morsel:
To set this compiler option in the Visual Studio development environment
Well, that would explain how this can lead to an increase in compiler efficiency!
You can't specify any additional options to the C# compiler via the IDE, and there's no way to specify a keycontainer on the "Signing Page".
Luckily, there is a way to specify a keycontainer without using the AssemblyKeyName attribute. One needs to close the C# project and open up the .csproj file for the particular project in an XML editor ("Notepad"). In the first <propertygroup> element one can add the following line, replaing [containername] with the name of the key container one wishes to use:
<keycontainername>[containername]</keycontainername>
Note that as tempting as it may be, you need to leave the value of the "SignAssembly" element as false. Apparently, "SignAssembly" really means "use an assembly key file".
Open up the project again and build the assembly, and it should be signed with the key that was installed into the container specified in the KeyContainerName.
?
This post originally appeared on an external website
I noted the following the other day when I was doing some C# development...
If one creates a new "Windows Application" and examines AssemblyInfo.cs, it has the following content:
// Version information for an assembly consists of the following four values:
//
// Major Version
// Minor Version
// Build Number
// Revision
//
[assembly: AssemblyVersion( "1.0.0.0" )]
[assembly: AssemblyFileVersion( "1.0.0.0" )]
However, if one creates a new "Class Library" and examines AssemblyInfo.cs, one sees the following:
// Version information for an assembly consists of the following four values:
//
// Major Version
// Minor Version
// Build Number
// Revision
//
// You can specify all the values or you can default the Revision and Build Numbers
// by using the '*' as shown below:
[assembly: AssemblyVersion( "1.0.0.0" )]
[assembly: AssemblyFileVersion( "1.0.0.0" )]
Of course, the '*' notation in the comments for the Class Library (in this case, at least) that incorrectly indicates the '*' is "shown below" is a remnant of Visual Studio .NET 2002 and Visual Studio .NET 2003, where the default for the AssemblyVersion attribute was a value like "1.0.*".
According to the AssemblyVersionAttribute Constructor on MSDN, specifying "1.0.*" sets the "build number" value to be equal to the number of days since January 1, 2000 local time, and "revision" to be equal to the number of seconds since midnight local time, divided by 2. Specifying "1.0.1.*" sets the "revision" to be equal to the number of seconds since midnight local time, divided by 2.
To remove the minor inaccuracy, one could probably change the inaccurate comment by modifying the project template at either %PROGRAMFILES%\Microsoft Visual Studio 8\Common7\IDE\ProjectTemplatesCache\CSharp\Windows\1033\ClassLibrary.zip\AssemblyInfo.cs, or AssemblyInfo.cs in %PROGRAMFILES%\Microsoft Visual Studio 8\Common7\IDE\ProjectTemplates\CSharp\Windows\1033\ClassLibrary.zip. Alternatively, one could change the values of AssemblyVersion and AssemblyFileVersion...
This post originally appeared on an external website
So I've been messing with the Enterprise Library for .NET Framework 2.0 - January 2006 a bit lately (see also patterns & practices: Enterprise Library: Home). Since I'm using strong-named assemblies, I needed to sign the assemblies from the Enterprise Library in order to use them. It seems, however, that this scenario was given little thought since it is quite tedious to do this. Ultimately, through sheer brute force I did manage to get them signed using a key container rather than a key file. Here's how...
Use Windows' "Search" function to find *.csproj in the root installation folder for the Enterprise Library ("C:\Program Files\Microsoft Enterprise Library January 2006" by default) and all sub-folders. Select all of the files (102 of them), right-click, and choose "Properties". Click the box to clear the "Read-only" check box, and "OK" the changes.

Then, open Visual Studio 2005 and use the "Find In Files" feature to find files containing a space, of type *.csproj, in the root installation folder for the Enterprise Library (again, "C:\Program Files\Microsoft Enterprise Library January 2006" by default) and all sub-folders. Also tick the "Display file names only" box.
The names of the 102 files will display in the "Find Results 1" area. In each (EACH!) CSPROJ project file, add ContainerName to the first section, as described in Signing Assemblies in Visual Studio 2005 with Key Containers . If I wouldn't have been so adept at the "click, paste, F8" trio (position the iBeam, paste the key container blurb, go to the next CSPROJ file), I probably would have automated the process with some code or something. Anyway, if this is all one does and one saves the files and then tries to build the Enterprise Library, one gets several CS1726 compiler errors.
Compiler Error CS1726 Error Message
Friend assembly reference 'reference' is invalid. Strong-name signed assemblies must specify a public key token in their InternalsVisibleTo declarations.
To get past the CS1726 errors, more details need to be added to the "InternalsVisibleTo" attribute for various assemblies - specifically, the public key. The public key can be obtained by starting a Visual Studio 2005 Command Prompt or SDK Command Prompt and using SN.EXE (the "Microsoft (R) .NET Framework Strong Name Utility") to extract the public key from the key container:
sn -pc ContainerName PubKeyFile
Then, SN.EXE is used again to display the public key:
sn -tp PubKeyFile
Copy the public key from the console to the clipboard and paste it into Notepad to do a bit of massaging. While you're at it, prefix the public key with ", PublicKey=" so you have something that looks like:
, PublicKey=002400000480000[...]559ea [truncated for brevity]
Copy that whole blurb to the clipboard. Next, use Windows' Search function to find all files named "AssemblyInfo.cs" in the root installation folder for the Enterprise Library and all sub-folders, containing the text "InternalsVisibleTo". Again, select all of the files (15 of them), right-click, and choose "Properties". Click the box to clear the "Read-only" check box, and "OK" the changes.
Then, bring up "Find In Files" in Visual Studio 2005 again, and search the root installation folder for the Enterprise Library for files named AssemblyInfo.cs containing "InternalsVisibleTo". Again, make sure the "Display file names only" box is checked. There should be 15 hits, but note that some files have more than one "InternalsVisibleTo" attribute. Place the iBeam in the attribute after the assembly name, and paste the public key. The attribute should change from something like:
[assembly: InternalsVisibleTo( "Microsoft.Practices.
EnterpriseLibrary.Caching.Tests" )]
to something like:
[assembly: InternalsVisibleTo( "Microsoft.Practices.EnterpriseLibrary.
Caching.Tests, PublicKey=002400000480000[...]559ea" )] [truncated for brevity]
Change all of the files, save the changes, and build the Enterprise Library. The library should now build successfully.
Note that you can use the "Build Enterprise Library" shortcut in the "Microsoft patterns & practices\Enterprise Library - January 2006" program group, but by default it builds a debug configuration. To build the release configuration, open a Visual Studio 2005 Command Prompt or SDK Command Prompt, navigate to the root installation folder for the Enterprise Library, and run BuildLibrary.bat specifying "Release":
BuildLibrary Release
Then, to copy the assemblies to the bin folder, run CopyAssemblies.bat, also specifying "Release":
CopyAssemblies Release
To copy the assemblies elsewhere, supply the location to CopyAssemblies.bat, like:
CopyAssemblies Release C:\EntLibJan2006
This post originally appeared on an external website
I have an annoying problem with Outlook 2003 crashing on me sometimes when I shut it down. Usually, if I'm closing Outlook, I'm leaving for the day. That means that I don't necessarily have the time nor the desire to try to figure out what's going on. I just clear the box that wants to restart Outlook, choose not to send the report to Microsoft (sorry!), and go on my merry way.
One day, I finally looked into things a bit. I chose to debug the problem, which kicked off VSJITDebugger.exe (Visual Studio Just-In-Time Debugger), and let me pick a new Visual Studio 2005 instance.
In the Output window of VS2005, I saw the following and tossed it into a "New Text Document":
> mscorwks.dll!MdaXmlMessage::SendDebugEvent() + 0x1c8 bytes
mscorwks.dll!MdaXmlMessage::SendMessage() + 0xf3 bytes
mscorwks.dll!MdaXmlMessage::SendMessagef() + 0xa9 bytes
mscorwks.dll!MdaLoaderLock::ReportViolation() + 0x13d bytes
mscorwks.dll!CanRunManagedCode() + 0xa64de bytes
mscorwks.dll!Unknown_Release() + 0x18 bytes
LookoutAddinShim.dll!DllGetClassObject() + 0x1a02 bytes
[Frames below may be incorrect and/or missing, no symbols loaded for LookoutAddinShim.dll]
LookoutAddinShim.dll!DllGetClassObject() + 0x1974 bytes
LookoutAddinShim.dll!DllGetClassObject() + 0x2650 bytes
LookoutAddinShim.dll!DllGetClassObject() + 0x3dbb1 bytes
LookoutAddinShim.dll!DllGetClassObject() + 0x22033 bytes
LookoutAddinShim.dll!DllGetClassObject() + 0x21f67 bytes
LookoutAddinShim.dll!DllGetClassObject() + 0x1dd01 bytes
LookoutAddinShim.dll!DllGetClassObject() + 0x1df5f bytes
ntdll.dll!_LdrpCallInitRoutine@16() + 0x14 bytes
ntdll.dll!_LdrUnloadDll@4() + 0x7569 bytes
kernel32.dll!_FreeLibrary@4() + 0x19 bytes
ole32.dll!CClassCache::CDllPathEntry::CFinishObject::Finish() + 0x25 bytes
ole32.dll!CClassCache::CFinishComposite::Finish() + 0x1599e bytes
ole32.dll!CClassCache::CleanUpDllsForApartment() + 0x63 bytes
ole32.dll!FinishShutdown() + 0x64 bytes
ole32.dll!ApartmentUninitialize() + 0x51 bytes
ole32.dll!wCoUninitialize() + 0x3f bytes
ole32.dll!_CoUninitialize@0() + 0x52 bytes
OUTLLIB.DLL!DllCanUnloadNow() + 0x13062 bytes
OUTLLIB.DLL!RenExitInstance@0() + 0x204 bytes
kernel32.dll!_BaseProcessStart@4() + 0x23 bytes
And of course I had to get going by the time all of the symbols were loaded, etc, so I closed the debugger and left for the day. But the output above seems to point to Lookout doing something naughty inside of the OS loader lock. (A list of naughty things can be found in the documentation for DllMain and "DllMain Restrictions" in "Mixed DLL Loading Problem".) I assume the message above is the implementation of the "Proposed Long-Term Solution" described in "Mixed DLL Loading Problem":
In addition to providing the managed module initializer mechanism to fix the loader lock problem in newly compiled images, this solution also provides checks to prevent the common language runtime from executing unsafe images that may have been built with old tools.
This would make sense, since LookoutAddinShim.dll is a mixed image - it is a COM component with dependencies on MSCOREE.DLL. In my case, it is using the .NET Framework 2.0, which presumably has incorporated the "Proposed Long-Term Solution" described in "Mixed DLL Loading Problem" as it certainly is "the next version of the common language runtime (after version 1.1)".
Generally, the "OS loader lock" issue is best dealt with by following the instructions specified in the Managed Extensions for C++ Reference at "Converting Managed Extensions for C++ Projects from Pure Intermediate Language to Mixed Mode".
I should note that I'm not sure what specifically caused Outlook to crash - the above is just a message that was in the Output window in Visual Studio 2005. It may or may not be the culprit.
This post originally appeared on an external website
I ran across an article in the Microsoft knowledge base that really got me worrying: PRB: "Can not Access File 'AssemblyName' Because It Is Being Used by Another Process" Error Message in ASP.NET. The shocker is in the CAUSE section:
CAUSE
This problem occurs because signed assemblies in the Bin directory are not supported.
What? Where is this documented (besides the KB article)? Why? And what versions of the .NET Framework does this apply to? The KB article states it applies to the .NET Framework 1.1 and 1.0 / ASP.NET 1.1 and 1.0, but the article's "Last Review" was on 2005-09-27 - before the .NET Framework 2.0 / ASP.NET 2.0 was officially released. Is the article simply waiting for an update? Another article that makes one wonder if the .NET Framework 2.0 / ASP.NET 2.0 is affected is PRB: "Access Denied" Error Messages When You Do Not Put Strong-Named Assemblies in the Global Assembly Cache. This article's "Last Review" was on 2004-01-24, but it states that it applies to "Microsoft Web Services Enhancements for Microsoft .NET 2.0". I'm probably being way too literal, but couldn't one at least glance at that and think it applies to the .NET Framework 2.0? Anyway, Tess Ferrandez writes in her blog "If broken it is, fix it you should":
...strong named assemblies, irrespectively of where they are loaded from are loaded into a shared domain (they are domain neutral)... ...Since the assemblies in the shared domain are not unloaded when the app domain unloads they may get locked if you are unlucky with timing. Locking issues most frequently occur with processes that frequently scan folders such as index server, virus scanning software or backup software... ...If a strong named assembly is used by multiple web applications and each application grants it varying permissions or if the permission grant varies between application domain restarts, you might see errors like ?Assembly .dll security permission grant set is incompatible between appdomains?...
That would explain the "Why" (article 813833 makes a similar statement, but Tess goes into more detail). But it's not clear if the .NET Framework 2.0 / ASP.NET 2.0 is affected until you look at the comments, where Tess states:
In 2.0 the assemblies are not loaded domain neutral [...] there was a very specific reason i mentioned 1.1. (and 1.0 for that matter)
and
the issue is due to the dlls being loaded in the shared domain in 1.0 and 1.1. which no longer occurrs in 2.0 [...]
An interesting comment to Tess' post points one to FxCop's AssembliesShouldHaveValidStrongNames rule. FxCop likes assemblies to be signed, but there's nothing that says they have to go in the GAC... Ouch.
This post originally appeared on an external website
[2006-09-29: Related post here...]
I was recently exposed to a "White Paper" (love the term...) called "Alternate Data Streams ? What?s Hiding in Your Windows NTFS?"
I was a bit disappointed as I was hoping to learn a bit more about alternate data streams. I really didn't pick up anything new, aside from the introduction of a few software utilities that can somewhat facilitate manipulation of ADS. A few things in the paper were left unexplored though.
The paper states:
When you use Microsoft Internet Explorer (at least through version 6) to download and save files from the Internet, the browser creates an ADS called Zone.Identifier. This file contains information about the Internet zone from which the file was downloaded.We have yet to discover why we might need that information, but that is what it does.
Without direcly stating that ADS is the underlying mechanism (it only states "The Web content zone information is saved together with the files only if the hard disk uses the NTFS file system"), Description of how the Attachment Manager works in Windows XP Service Pack 2 describes what the information in the ADS is used for. Further, this behavior is new with Windows XP Service Pack 2, and was not present in previous versions of IE ("at least through version 6").
The paper also states:
In the Windows XP Windows Explorer, if you choose the View ?> Thumbnails option for pictures, it appears to create the thumbnail as an ADS. These files have names similar to {4c8cc155-6c1e-11d1-8e41-00c04fb9386d}. Very informative, as you can see. Note that we are not certain that this is the thumbnail, since we?ve yet to find a way to open one of those files. However, using the utilities discussed above, we can clearly see that choosing View ?> Thumbnails creates ADSs behind picture files.
I tried to do just what the author described, but I was unable to see any files OR streams named with the {xxxxxxxx-xxxx-xxxx-xxxx-xxxxxxxxxxxx} convention. It's a GUID, of course - it's not meant to be informative - just unique. The statement about not being able to "find a way to open one of those files" is rather interesting. Try a binary editor or even a simple text editor like Notepad - what's in the stream?
I decided to do a bit of digging, and found plenty of references to the GUID the author mentioned - {4c8cc155-6c1e-11d1-8e41-00c04fb9386d} - in fact, Googling the GUID (alliteration?) yields about 1000 results. That seemed like a lot of hits for a GUID that, based on the author's description, was a filename or stream name for a thumbnail.
Turns out that running FileMon on my system and filtering for "4c8cc155" turns up a bunch of hits (er... misses?) when I start browsing the file system with Windows Explorer. Specifically, an attempt was made to open an ADS named {4c8cc155-6c1e-11d1-8e41-00c04fb9386d} on each folder I browsed to, and each file that I selected. So it would seem that something else is going on here.
I wondered what the shell (explorer.exe) would do if it found such a stream on a folder or file, so I made one. Nothing significant happened. Then I tried simply changing the view of a folder (without the ADS {4c8cc155-6c1e-11d1-8e41-00c04fb9386d}) to "Thumbnails". FileMon indicated that explorer.exe tried to open the ADS in question on the folder. Nothing earth shattering here.
Next, I created a test folder with a test file - molotov.eee. I did a "Properties" on the file, and hit the Summary tab. I entered some garbage in the Title and Subject fields, and hit "Apply". FileMon showed that explorer.exe indeed created a stream named {4c8cc155-6c1e-11d1-8e41-00c04fb9386d} on molotov.eee. It would appear that our mysterious GUID-named stream is related to the "Summary" metadata that one can specify for most / all files.
Interestingly, tossing garbage in the {4c8cc155-6c1e-11d1-8e41-00c04fb9386d} stream causes Explorer to not display the Summary tab when one views the Properties of the subject file. It must not recognize the format, decide that the stream is used for something else, and in the interest of stability or not overwriting data chooses not to provide an interface to view the uninterpretable stream. A 0 byte stream named {4c8cc155-6c1e-11d1-8e41-00c04fb9386d} on a file does not have an impact on whether or not the shell chooses to display the Summary tab in the file's Properties. In fact, the stream that Explorer creates is 0 bytes. The real meat of the Summary information, then, must be in the other stream that's created - the ♣SummaryInformation stream - which does vary in size based on what is entered in the Summary fields.
[Added 2006-09-19: Additional things to try here...]
This post originally appeared on an external website
It seems that a LOT of people are getting error 0x8ddd0009 with Microsoft Update or Windows Update, and are looking for fixes to the problem.
Previously, I had noted that I had gotten around the problem by correcting the system time on the affected computer. But apparently that's not the only "fix" for the problem. Given that it doesn't do the trick for everyone, here is a compilation of suggestions that I have run across. Note that I haven't tried all of them and I can't vouch for their accuracy. Some suggestions involve the use of a 3rd party program or utility. Use them at your own risk.
If you have gotten the 0x8ddd0009 error from Microsoft Update or Windows Update and something listed here fixes it, please chime in. Also, if you did something not listed here and it took care of the problem, please share your resolution with others.
I can't find any reference to 8ddd0009 OR 0x8ddd0009 in the Microsoft knowledge base, so we're pretty much going off of community references here.
While most of the people reporting 0x8ddd0009 seem to be running Windows 2000 with some recent service pack (3 or 4), some are running Windows XP SP2.
To restate, I fixed my problem by ensuring that the system time on the affected computer was accurate - it had been about 22 minutes off. Once I corrected the time, the problem went away.
Another thing to do is to make sure that the computer that is having problems has sufficient free space available on the disk. I'll grab 1 GB out of the air and toss it in here - make sure there's 1 GB of free space on the disk. Just to be safe...
Several people report that uninstalling Windows Installer 3.1 resolved the 0x8ddd0009 error. To uninstall Windows Installer 3.1, use the "Add or Remove Programs" applet in the Control Panel, and find "Windows Installer 3.1 (KB893803)" in the list, and click the "Remove" button. Alternatively, running "%WINDIR%\$MSI31Uninstall_KB893803v2$\spuninst\spuninst.exe" from Start --> Run may do the trick.
Running regsvr32 /u "%systemroot%\system32\mobsync.dll" has apparently worked for at least one individual; Microsoft Knowledge Base article "Event ID 4100 appears repeatedly in Event Viewer details this approach (not in the context of the 0x8ddd0009 error, though), and also the implications:
After you unregister Mobsync.dll, Client Side Caching (CSC) no longer works. The behavior described in the "Symptoms" section of this article does not affect CSC functionality, but unregistering Mobsync.dll does
If that doesn't do the trick, one should be able to UNDO the unregistration (???) of Mobsync.dll by running regsvr32 "%systemroot%\system32\mobsync.dll". Might be worth a shot...
Other people report that downloading / installing / running a program called "Dial-A-Fix" (apparently free) and using it to fix "Windows Update" (whatever that program considers "Windows Update") fixes the problem. The program can likely be found here. And here are extensive instructions for using the program to fix the problem.
Re-running the "Connection Setup Wizard" (presumably, in IE's Tools --> Internet Options --> Connections tab --> "Setup..." button; it can also be run by tossing "rundll32.exe netshell.dll,StartNCW" in the Start --> Run box) is reported to have resolved the 0x8ddd0009 error for several people.
Another thing that has worked in certain cases is running regsvr32 msxml3.dll from the Start --> Run box or a Command Prompt.
Something else to try is to run the following commands from a Command Prompt (Start --> Run --> Cmd):
proxycfg -d
net stop wuauserv
net start wuauserv
Disabling any firewalls might be another thing to try.
Some have indicated that following the instructions in Microsoft Knowledge Base article Error messages that you may receive when you try to download and install updates from the Windows Update Web site, from the Microsoft Update Web site, or from a WSUS server: "0x800704DD," "0x80240020," or both took care of the 0x8ddd0009 error for them.
Stopping the "Automatic Updates" service (from the Services management console snap-in - Start --> Run --> Services.msc, or by running net stop wuauserv), and deleting (renaming is less destructive, I suppose) the %windir%\SoftwareDistribution folder can also resolve various issues with Microsoft Update / Windows Update.
On a more drastic note, uninstalling Windows XP Service Pack 2 and then reinstalling it took care of the 0x8ddd0009 error for at least one person.
Again, if you have gotten the 0x8ddd0009 error from Microsoft Update or Windows Update and something listed here fixes it, please chime in. Also, if you did something not listed here and it took care of the problem, please share your resolution here so that others may benefit.
Sort by Trending


