As a former-aspiring-network-engineer, I've seen a few goodies that hackers of any hat color enjoy. Be familiar with these tools.
Some good ones to start with are:
nmap - network mapper and port discovery tool
(start out with one with a GUI like Zenmap or nmapFE or you'll be lost in the beginning).
http://insecure.org
WireShark - packet sniffer
(Did you know that many IMs pass data in unencrypted HTML?)
http://www.wireshark.org/
Kismet - wireless packet sniffer/network analyzer
http://www.kismetwireless.net/
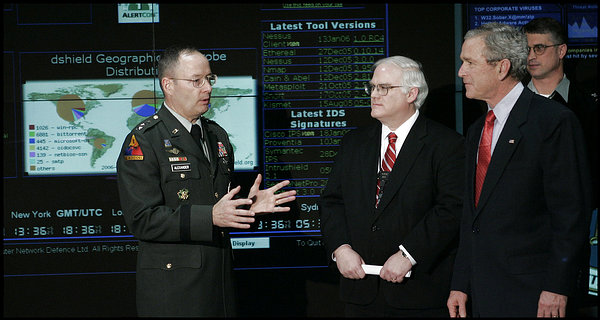
The list goes on, but this should be handy:
http://nmap.org/images/wash-post-nsa.jpg (You might have to squint.)
Another good reference:
http://en.wikipedia.org/wiki/Penetration_test
And finally, if you really want to get into it, check out the Black Hat conferences, and try lurking in some of the freakier IRC rooms (No, I don't know them. I'm just a guy who put his Cisco certs on hold to keep a steady job.)
Back to reality and white collar jobs:
I encourage taking the CCNA, CISSP courses as the principles presented, while flavored for Cisco, are applicable in any environment.
Security + from CompTIA is also a must.
As far as programming, do as you like, but as an aside, NOD32 (renowned as one of the badassest AntiViruses out there) is written in pure Assembler. I recommend healthy doses of C and C++ (especially in the GNU arena) as they're generally considered tighter and faster than most other languages (because most other languages either started out their lives as scripting languages for interpreters or take cross-compatibility to extents that speed and size-constraints are sacrificed).
Best of luck, friend.