


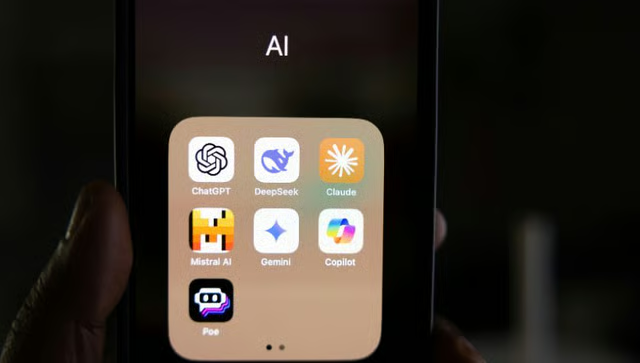
Sweden’s Government Offices are blocking direct browser access to ChatGPT and Claude on staff computers while keeping Microsoft Copilot available for official work.
The Swedish Government Offices, which support the prime minister and government ministries, blocked browser access to OpenAI’s ChatGPT and Anthropic’s Claude on staff computers on Monday, Oct. 26, according to Sveriges Radio and an email the government sent to SVT.
Officials want employees to use AI services approved by the Government Offices. Mikael Wettercrantz, the Government Offices’ director of digitalization, warned on the internal staff network that using AI services without formal agreements could have “consequences for our information security,” Sveriges Radio reported.
Separately, an internal audit at the Swedish Transport Administration identified widespread, risky use of about 10 AI services. The audit found problems involving both the sensitivity of information employees entered into AI tools and how they handled the resulting responses, according to Sveriges Radio.
Why Copilot Remains Available
Microsoft Copilot remains approved after a government review, with additional security measures introduced following the assessment. Officials have not disclosed the specific changes.
The distinction centers on organizational approval, contractual protections and security controls, rather than establishing that one AI model is inherently safer than another. Formal agreements can define how providers process information and what protections apply when employees use AI tools.
Some Government Offices employees retain access to ChatGPT and Claude through Intric, an approved AI platform, SVT reported. The platform’s supplier announced in July that it had won a contract to provide its AI platform to the Government Offices.
The reports do not specify how many employees retain access through Intric or detail the security controls in that deployment.
More Swedish agencies are tightening AI access
The Government Offices are not acting alone. Sveriges Radio reported that the Swedish Tax Agency and the National Board of Institutional Care have also restricted AI services. The Swedish Enforcement Authority is considering its own measures.
The Government Offices had previously restricted use of DeepSeek, according to Sveriges Radio. Elsewhere, the European Parliament disabled built-in AI features on staff-issued devices in February 2026 over cybersecurity and data-protection concerns, TechRadar reported.
More must-read AI coverage
- SS&C Intralinks DealCentre AI vs. Datasite: Which platform is built for the future of dealmaking?
- SS&C Intralinks FundCentre AI vs. Juniper Square: Which platform better supports modern private markets fund managers?
- Why Data, Not Models, Determines AI Success
- The Rise of the AI-Native Factory: How Physical AI Is Transforming Manufacturing
What IT teams should review before approving AI access
The restriction applies to Government Offices work computers, rather than consumers or private businesses across Sweden. For IT teams adopting generative AI, it offers a reason to review which services employees use, which accounts they sign in with, and what information they submit.
Approval should cover the specific service and deployment. Teams should document which accounts, interfaces, integrations, and tasks are permitted so employees understand when a tool is approved for work. Access through a personal account should not be assumed to carry the same protections as an organization’s contracted service.
Before allowing confidential information into an AI tool, organizations should review contractual terms, data retention, model-training provisions, administrative controls, and any connected applications. Employees need clear examples of what they may submit and which information requires additional authorization.
An approved alternative also needs to support the work employees actually do. IT teams should provide a straightforward process for requesting new capabilities, reporting accidental disclosures, and checking generated material before it informs consequential decisions.
The practical lesson is to make approved AI use both understandable and workable. Blocking a website addresses one access route; a useful workplace policy also establishes who can use each service, what data it may handle, and who is responsible for reviewing its output.